Gong DPA and Security Review: Compliance Analysis 2027
Written by
Ishan Chhabra
Last Updated :
November 17, 2026
Skim in :
13
mins
In this article
Still got questions?
Come discuss this article with me.
Hi, I'm Ishan, Founder and CEO of Oliv.
I'm always up for a conversation about revenue intelligence, AI agents, or what's actually working (and what's not) across revenue teams.
I'd love to hear your perspective.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Meet Oliv’s AI Agents
Hi! I’m, Deal Driver
I track deals, flag risks, send weekly pipeline updates and give sales managers full visibility into deal progress
Hi! I’m, CRM Manager
I maintain CRM hygiene by updating core, custom and qualification fields all without your team lifting a finger
Hi! I’m, Forecaster
I build accurate forecasts based on real deal movement and tell you which deals to pull in to hit your number
Hi! I’m, Coach
I believe performance fuels revenue. I spot skill gaps, score calls and build coaching plans to help every rep level up
Hi! I’m, Prospector
I dig into target accounts to surface the right contacts, tailor and time outreach so you always strike when it counts
Hi! I’m, Pipeline tracker
I call reps to get deal updates, and deliver a real-time, CRM-synced roll-up view of deal progress
Hi! I’m, Analyst
I answer complex pipeline questions, uncover deal patterns, and build reports that guide strategic decisions
TL;DR
Gong's September 2026 DPA makes you the controller and Gong the processor, with a 5 business day sub-processor objection window and deletion 30 days after the contract ends.
Gong holds SOC 2 Type II, ISO 27001, 27017, 27018, 27701 and ISO 42001; verify scope and dates in the Trust Center rather than trusting blogs.
New Gong customers can choose US or EU data centers on AWS, but processing can still happen in the US, Israel, Ireland and sub-processor regions.
Recording consent stays with you; CIPA allows $5,000 per violation and class actions now target AI call vendors.
The DPA is silent on AI model training, so request a written AI rider; the EU AI Act bans workplace emotion recognition.
Run the review over 90 days with named owners, budget for add-ons, and compare Oliv AI's single governed agent layer against reviewing several apps.
A RevOps manager at Oliv AI was looking at website analytics one morning and noticed something odd. An enterprise prospect's team had skipped the pricing page entirely. They went straight to the footer, opened the privacy policy, and read it closely before they ever booked a call. That is how security review starts now. It starts before the first meeting, and it starts with the paperwork.
If you are reviewing Gong, here is the short answer. Gong's Data Processing Addendum (DPA) and certifications are a solid enterprise baseline. The real review work sits in five places: recording consent, AI data use, data residency, sub-processor tracking, and add-on cost. Most of that risk belongs to you, because under GDPR you are the controller. This guide walks through the September 2026 DPA in plain language and shows you what to check, who owns it, and how to finish the review without stalling the deal for a quarter.
Q1: What Is the Gong DPA and What Does It Actually Commit Gong To? [toc=1. What the Gong DPA Says]
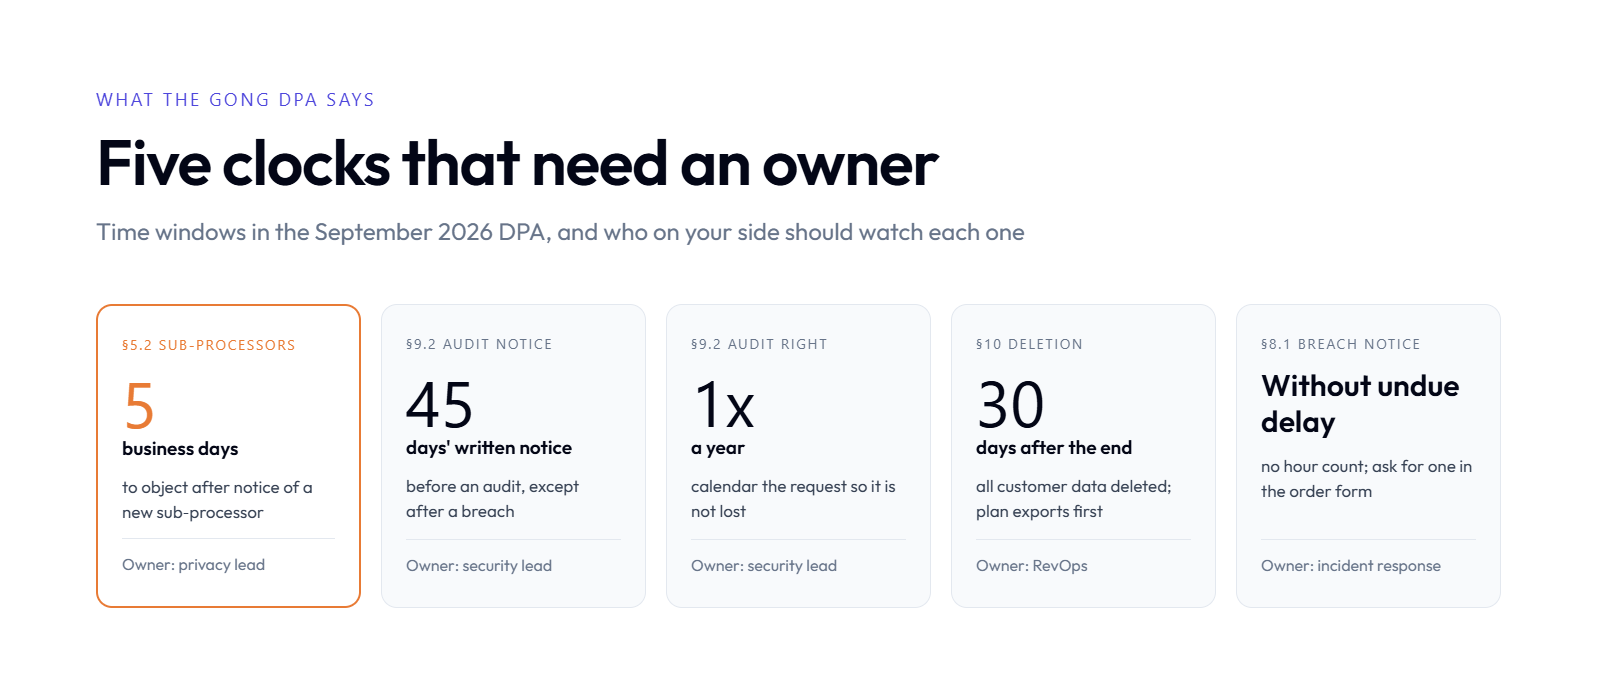
Each time window in the Gong DPA needs a named owner on your side.
The Gong DPA is the Data Processing Addendum that forms part of Gong's terms and conditions. It names the customer as the controller and Gong as the processor of personal data in calls, emails, and CRM records. The version published on gong.io is marked "last updated September 2026" (Gong DPA). It sets transfer terms for the EU, UK, and Switzerland, a 5 business day window to object to new sub-processors, audit rights once a year on 45 days' notice, breach notice "without undue delay", and deletion of customer data 30 days after the contract ends (Gong DPA).
📄 Who does what under the DPA
A controller decides why and how personal data is used. A processor handles that data only on the controller's instructions. Under section 2.1 of the DPA, your company is the controller (the "business" under the California Consumer Privacy Act, or CCPA) and Gong is the processor (the "service provider") (Gong DPA).
There is one exception worth flagging. For Gong Enrich, the DPA's Schedule 2 makes Gong an independent controller of enrichment data (Gong DPA). If your team uses Enrich, that data sits under Gong's own privacy decisions, not only yours.
⚠️ The sensitive data line
Section 2.3 says the services "are not intended for the Processing of Sensitive Data" (Gong DPA). That is a statement of intent, not a technical block. Health details, financial account numbers, or union membership can still come up on a sales call. Your team carries the duty to keep that data out or to handle it lawfully under section 2.4 (Gong DPA).
⏰ The clause-to-action table
These are the time windows in the DPA that need a named owner on your side.
Gong DPA Clauses and Owners
DPA clause
What it says
Who should own it
Sub-processors (§5.2)
You may object within 5 business days of notice of a new sub-processor
Gong notifies "without undue delay"; details may arrive in phases
Incident response owner
Audit (§9.2)
Once a year, 45 days' written notice, except after a breach
Security lead, calendar the request
Deletion (§10)
All customer data deleted 30 days after termination or expiry; backups isolated
RevOps, plan exports before the end date
Changes (§14)
Either party may request changes on 45 days' notice; 30 days to agree
Legal
💡 What this means on Monday
The DPA gives you no hour count for breach notice. If your own policy needs one, such as 72 hours, ask for it in your order form. The 5 business day objection window is short, so the sub-processor page needs an owner, not a quarterly glance.
Oliv AI sees the same pattern in its own enterprise security reviews. The DPA is rarely what blocks a deal. The missing owner for each clause is. Oliv AI publishes its own trust material at trust.oliv.ai, so you can run the same clause-to-owner exercise on us side by side.
Q2: How Does Gong Handle GDPR, CCPA and International Data Transfers? [toc=2. GDPR, CCPA and Transfers]
Gong handles GDPR and CCPA through its DPA, which assigns the customer the controller role and Gong the processor role (Gong DPA). For data leaving the European Economic Area, the DPA uses the EU Standard Contractual Clauses (SCCs) under Decision 2021/914, Modules One to Four, governed by Irish law (Gong DPA). It adds the UK Addendum issued by the Information Commissioner's Office and a Swiss schedule under the Federal Act on Data Protection (FADP) (Gong DPA). Gong also states it is certified under the EU-U.S. Data Privacy Framework (Gong security FAQ).
🌍 The transfer stack, in plain words
Standard Contractual Clauses are pre-approved contract terms from the European Commission. They let personal data move to a country without an EU "adequacy" decision. Here is how Gong's stack lines up.
Gong Data Transfer Mechanisms by Region
Region
Mechanism in the Gong DPA
Source
EU and EEA
EU SCCs, Decision 2021/914, Modules One to Four, Irish law and courts
Part 4 of the schedule adds extra safeguards, including encryption in transit and at rest and rules for government access requests (Gong DPA).
⚖️ CCPA terms
Under section 2.5, Gong may not sell or share personal information as those terms are defined in the CCPA (Gong DPA). Gong processes data only on your documented instructions, and anonymization is listed as a permitted instruction under section 2.4 (Gong DPA).
✅ What stays with you as controller
Paper compliance on Gong's side does not move your duties. You still own these tasks.
Lawful basis. Decide and record why you process call data, such as legitimate interest or consent.
Data subject requests. Respond when a prospect asks to see or delete their data. Gong's FAQ points to API and in-app tools for the right to be forgotten (Gong security FAQ).
Notices. Tell prospects and employees that calls are recorded and analyzed.
Records of processing. List Gong and its sub-processors in your own records.
I have watched a privacy lead approve a vendor on the strength of its DPF certificate, then realize nobody owned deletion requests. The certificate was fine. The workflow was missing.
Oliv AI states that it is GDPR and CCPA compliant and offers a full open export policy with no data lock-in. That makes access and deletion requests simpler to answer, because the data is not trapped in one app's format.
Q3: Which Security Certifications Does Gong Hold in 2027, and How Do You Verify Them? [toc=3. Gong Security Certifications]
Gong's help center lists a SOC 2 Type II report, ISO/IEC 27001, 27017, 27018, and 27701 certificates, and a listing in the Cloud Security Alliance (CSA) STAR Registry (Gong security FAQ, Gong security features). Gong also lists ISO 42001:2023, the AI management system standard, which it says it earned in June 2025 (Gong security features, Gong responsible AI). Reports and certificates are available through the Gong Trust Center, where you request access before review (Gong Trust Center).
📋 What each certificate covers
Each certificate answers a different question. None of them answers all of them.
What Each Gong Certification Proves
Certification
What it shows
What it does not prove
SOC 2 Type II
An auditor tested security controls over a period of time
That your tenant settings are correct
ISO 27001
A managed information security system exists and is audited
Control depth for every product
ISO 27017 / 27018
Cloud security controls and protection of personal data in the cloud
Your consent workflow
ISO 27701
A privacy information management system on top of 27001
Lawful basis for your processing
ISO 42001
An audited AI governance program
Whether your calls train any model
CSA STAR
A published cloud security self-assessment or audit
Ongoing compliance between audits
🔍 How to verify, step by step
Request the package. Ask for the SOC 2 Type II report, ISO certificates, the CAIQ (the Cloud Security Alliance's standard security questionnaire), and the pentest summary through the Trust Center (Gong Trust Center).
Check the audit window. A SOC 2 Type II report covers a set period. Note the end date and ask for a bridge letter if it is older than six months.
Check scope. Confirm the products you buy, such as Engage or Forecast, sit inside the certified scope.
Check certificate dates. One 2025 third-party review said Gong's ISO 27001 certificate expired in October 2025. Gong's own pages now list ISO/IEC 27001:2022 (Gong Trust Center). Confirm the current certificate in the Trust Center rather than trusting any blog, including this one.
Log exceptions. Read the auditor's exceptions section, not only the opinion letter.
🧭 My honest read
Gong is a market leader, and it holds the certifications a market leader should hold. I would not build a security case against Gong on missing paperwork. The questions that matter sit in consent, AI data use, and residency, which the next sections cover.
Oliv AI is SOC 2 Type II certified and publishes its trust material at trust.oliv.ai. Ask Oliv AI for the same package you ask Gong for, and compare the audit windows and scope line by line.
Q4: Where Is Your Sales Data Stored and How Is It Protected? [toc=4. Data Storage and Protection]
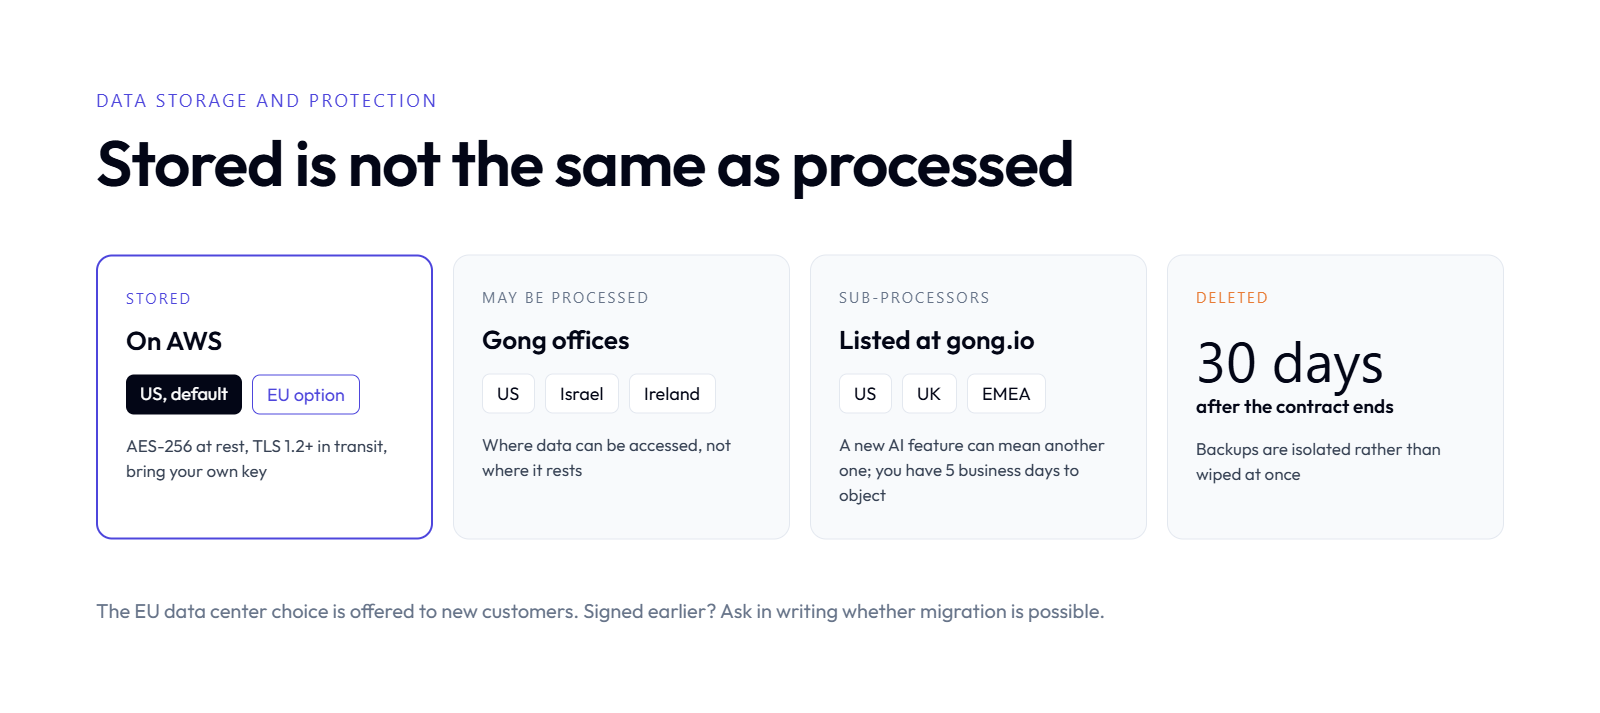
Where Gong stores data and where it can be processed are two different questions.
Gong is hosted on Amazon Web Services (AWS). Gong's help center says new customers can choose US or EU data centers, with the US as the default (Gong security FAQ). Data is encrypted in transit with at least TLS 1.2 and at rest with AES-256, and customers can bring their own encryption key (BYOK) (Gong security features). Gong's offices in the US, Israel, and Ireland may process data, and its sub-processors sit in the US, UK, and EMEA (Gong security FAQ). Customer data is deleted within 30 days of contract end (Gong DPA, Gong security FAQ).
🗺️ How it used to work
For years, the standard answer on Gong storage was "it lives in the US." Many 2025 reviews, including the earlier version of this guide, said all customer data was stored in the United States. EU security teams treated that as a blocker or paid for workarounds.
That picture is now out of date. Gong's FAQ confirms the US and EU choice for new customers (Gong security FAQ). If you signed before that option existed, ask your account team in writing whether migration is possible and what it costs.
🔐 Storage is not the same as processing
Here is the part that catches teams out. Where data rests is one question. Where it can be accessed or processed is another.
Storage: US by default or EU on request, on AWS (Gong security FAQ).
Processing: Gong offices in the US, Israel, and Ireland (Gong security FAQ).
Retention: set by you and changeable at any time, per Gong's security page (Gong security features).
Deletion: 30 days after the contract ends, with backups isolated rather than wiped at once (Gong DPA).
⚠️ What changed with AI
Conversation intelligence used to mean a recording, a transcript, and a dashboard. Now each call feeds AI summaries, trackers, and agents. Every new AI feature can mean another processing step, and sometimes another sub-processor. The map of where your data travels grows each quarter, even if the storage region never changes.
Customer reviews show the operational side of this. One reviewer noted the cost of leaving.
"if you stop working with thew tool you lose the data" Verified User Gong - G2 Verified Review [3/19/2026]
"I cannot download all the data myself unless we upgrade the plan" Verified User Gong - G2 Verified Review [10/3/2025]
🧩 How Oliv AI approaches data flow
Oliv AI is an AI-native revenue intelligence platform that keeps account and deal context in one governed layer, the GTM Context Graph, instead of copying it across several bolt-on apps. Oliv AI encrypts data with AES-256 at rest and TLS 1.2+ in transit, and its open export policy means you keep your data when you leave. Fewer copies in fewer apps means a shorter data map for your security team to approve.
Q5: Which Access Controls and Audit Features Matter for an Enterprise Rollout? [toc=5. Access Controls and Audit]
Gong supports single sign-on (SSO) through SAML 2.0, OAuth 2.0, and OpenID Connect, plus SCIM provisioning for automatic user setup and removal (Gong security features). It ships four built-in roles (Collaborator, Standard user, Business administrator, and Technical administrator) and granular permission profiles by person, team, or group (Gong security features). The Gong Audit API exports activity logs in JSON, covering platform use and Gong staff access to customer data (Gong security features). Gong runs third-party penetration tests, a bug bounty, and a Vulnerability Disclosure Program at vdp.gong.io (Gong security features).
🧑💼 How access control used to work
The classic rollout went like this. IT connected SSO, RevOps created users by hand, and every manager got broad access "for now". Six months later, nobody could say who could hear which calls. A departed rep's account was still active because nobody owned offboarding.
That was the real risk in conversation intelligence. The controls existed. They were simply switched on late, or not at all.
✅ What to switch on in week one
Use this list before the first call is recorded.
SSO, enforced. Turn off password login once SSO works.
SCIM provisioning. SCIM (System for Cross-domain Identity Management) creates and removes users from your identity provider, so leavers lose access the same day.
Permission profiles. Restrict call access by team. Sales managers rarely need every CS call.
Audit API export. Send logs to your security tool weekly, not only after an incident.
BYOK, if policy requires it. Bring your own key gives you control over encryption keys (Gong security features).
⚠️ What changed: agents need permissions too
Here is the shift most security reviews miss. In 2027, people are not the only actors touching call data. AI agents now read transcripts, draft emails, and update CRM fields. A role model built for humans does not tell you what an agent may do without asking.
Ask every vendor, Gong included, a direct question. Which AI features can write to our CRM or send messages on their own, and where is that logged?
🛡️ How Oliv AI splits agent permissions
Oliv AI builds the permission model into its two super-agents. Olivia, Oliv AI's Chief of AI Staff, works on an "Ask before acting" model for AEs, BDRs, AMs, and CS managers. Oliver, the Chief AI GTM Engineer, works on "Act without asking" for RevOps and sales leaders who own the playbook.
Oliv AI's agent harness lists guardrails, audit and security, and monitoring and logging as core parts. That gives your security team one place to see what an agent did and why. We designed it that way because a human role chart cannot govern software that acts.
"The Analyst agent allows me to understand everything I need with just one click, eliminating the long wait time I used to have with RevOps to get answers." Verified User Oliv AI G2 - Verified Review [6/17/2026]
Q6: Who Owns Call Recording Consent, and What Changes in Two-Party Consent States? [toc=6. Recording Consent]
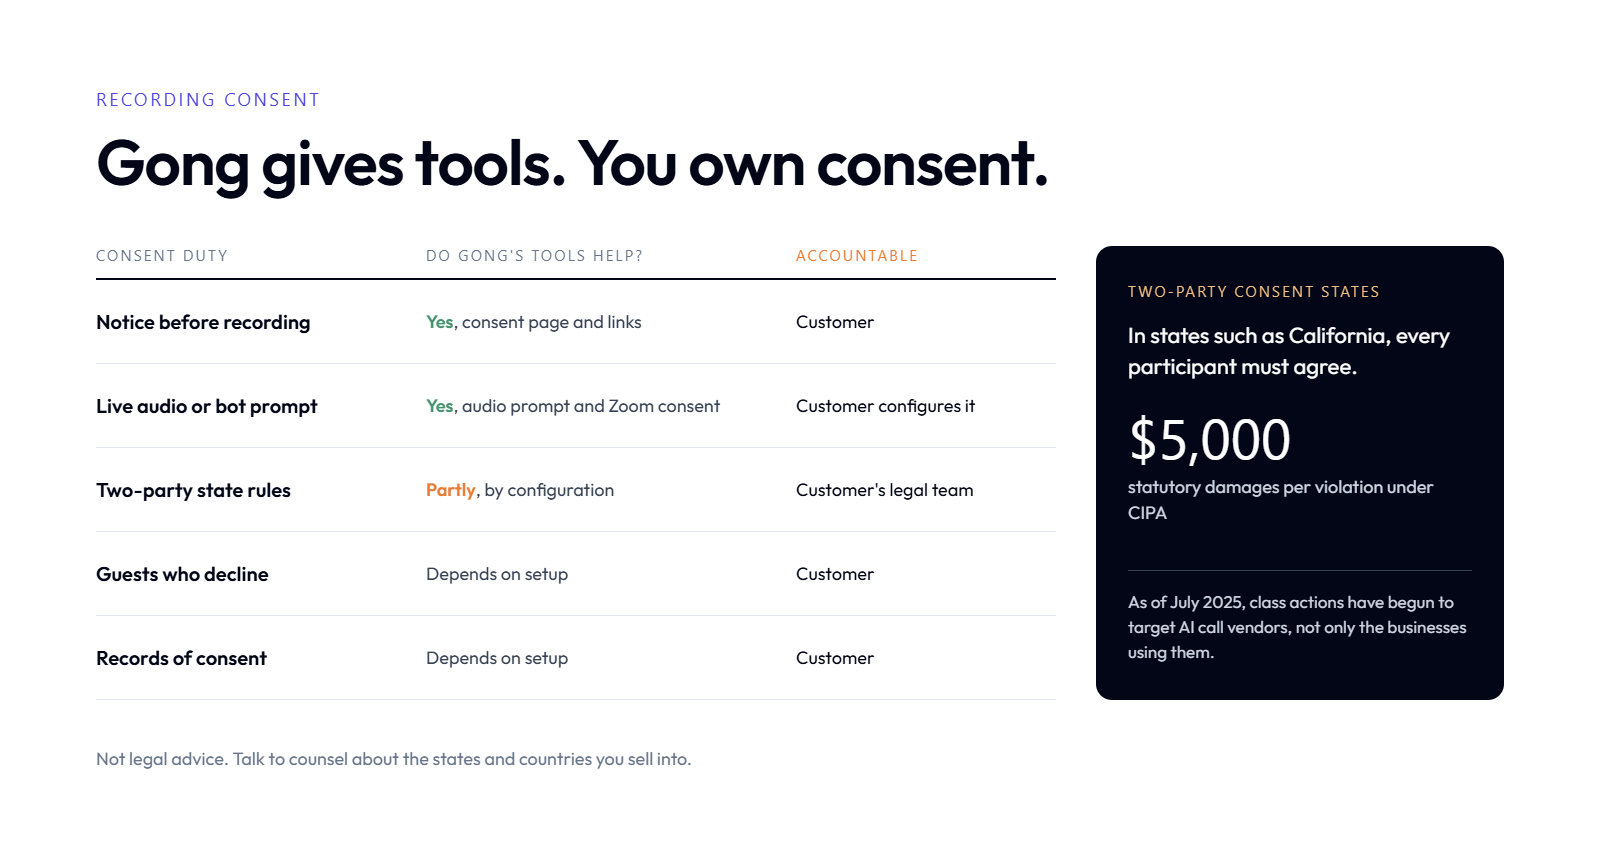
Gong provides consent tools, but the customer stays accountable for recording consent.
The customer owns recording consent. Gong provides tools that help, including consent links, a personalized consent page, and audio prompt or Zoom-based consent options (Gong Trust Center). Gong's FAQ says sales calls can be recorded "in compliance with the right workflows", which leaves configuring those workflows to the customer (Gong security FAQ). In two-party (all-party) consent states such as California, every participant must agree. California's Invasion of Privacy Act (CIPA) allows $5,000 in statutory damages per violation (Holland & Knight).
📞 How consent used to work
For years, the standard answer was a line in the calendar invite and a "this call may be recorded" notice. Legal signed off once. Nobody checked whether the prompt fired on every platform, or for every guest who joined late.
That worked because lawsuits targeted the company on the call, and most claims went nowhere.
❌ What that cost
Now the targets have changed. Holland & Knight reported in July 2025 that class actions have begun to target AI call vendors, not only the businesses using them (Holland & Knight). Suits against Cresta and ConverseNow claim that AI tools captured and analyzed calls without valid consent (Holland & Knight, Fisher Phillips).
In August 2025, a federal court in Northern California denied ConverseNow's motion to dismiss a CIPA class action (Fisher Phillips). Commentators also question whether generic "may be monitored for quality" notices are enough once AI analysis is involved (Fisher Phillips). To be fair, results differ. In February 2025, a court dismissed a CIPA claim against Talkdesk because the calls were not private enough to support standing (Fisher Phillips).
I am not a lawyer, and this is not legal advice. Talk to counsel about the states and countries you sell into.
⏰ What changed with AI capture
Recording is no longer one Zoom call. Revenue teams now capture mobile calls, in-person meetings, and chat. Each new channel needs its own consent moment, or the risk travels with the data.
🎙️ How Oliv AI handles consent-first capture
Oliv AI captures context across five ways revenue teams communicate, including in-person meetings. For physical meetings, Oliv AI's partnership with Plaud brings what Oliv AI calls ambient, consent-first capture. The point is simple. Consent should be designed into the capture step, not added as a footer later.
Q7: How Does Gong Use Your Call Data for AI, and What Does the EU AI Act Change? [toc=7. AI Data Use and the EU AI Act]
Gong's DPA does not address whether customer data trains AI models (Gong DPA). Gong holds ISO 42001, the AI management system standard, earned in June 2025 (Gong responsible AI). Gong points customers to the AI section of its Trust Center for AI data practices (Gong security features, Gong Trust Center). The independent VerifyWise AI Trust Index grades Gong "B" and notes that public policy does not state whether inputs are kept out of model training (VerifyWise). Under the EU AI Act, workplace emotion recognition has been prohibited since February 2, 2025 (EU AI Act).
🤖 How AI review used to work
Two years ago, the AI question in a security review was one checkbox. Does the vendor use AI? Yes. Next question.
That was fine when AI meant a transcript and a keyword tracker. It is not fine when AI summarizes every deal, scores reps, and drafts customer emails.
❌ Where the gap is now
ISO 42001 proves that Gong runs an audited AI governance program (Gong responsible AI). It does not tell you whether your calls train a shared model. Even Gong's own AI governance post lists "Can I prevent certain data from being used in AI prompts and training?" as a question customers should ask (Gong AI governance). That is a good question. Ask it in writing.
Here is the AI rider language I would request in the order form.
Customer data is not used to train models shared with other customers.
Customer may opt out of AI features by workspace or team.
Gong lists every AI sub-processor and its region.
Gong gives notice before a new AI feature processes customer data.
⚖️ What the EU AI Act changes
The EU AI Act is Regulation (EU) 2024/1689 (EU AI Act). Article 5(1)(f) bans AI that infers the emotions of people at work, except for medical or safety reasons. That ban has applied since February 2, 2025 (EU AI Act). Article 50 transparency duties, which cover telling people about emotion recognition, apply from August 2, 2026 (EU AI Act).
For revenue teams, the practical question is narrow. Does any feature infer a rep's emotion from their voice? If your reps are in the EU, switch that feature off or get a written legal view. Text-only sentiment on emails is generally treated differently, but confirm it with counsel.
🧠 How Oliv AI approaches AI data use
Oliv AI runs more than 100 fine-tuned small language models (SLMs), each trained for one revenue question, such as pains, decision makers, or budget. Oliv AI reports under 1% hallucinations in production for this narrow design. Narrow models do one job, which makes "what does this model see and why" an easier question to answer in review.
"I love how Oliv AI goes beyond simple call transcription to actually interpret and extract actionable insights from every interaction." Verified User Oliv AI G2 - Verified Review [7/8/2026]
Q8: What Hidden Costs and Operational Risks Come With a Gong Security Setup? [toc=8. Hidden Costs and Risks]
Gong does not publish list prices, so security costs show up during negotiation. Vendr's Gong pricing data estimates dedicated regional hosting at $10,000 to $25,000 a year, custom compliance requirements at $15,000 to $50,000, and enhanced audit trails at $5,000 to $15,000 a year (Vendr). The same data puts custom SSO setup at $2,000 to $5,000 and SCIM setup at $1,000 to $3,000 (Vendr). Operational risks include CRM storage load from synced call data and the overhead of tracking sub-processor changes.
💸 How the bill used to look
A typical Gong budget covered seats and a platform fee. Security lived in a separate column that nobody priced. Then the EU team asked for regional hosting, legal asked for longer audit logs, and IT asked for custom SSO.
Each request was small. Together, they changed the deal.
💰 The add-on ranges to budget for
These are third-party estimates, not Gong list prices. Treat them as a starting point for negotiation (Vendr).
Estimated Gong Security Add-On Costs
Item
Estimated cost
Dedicated regional data residency
$10,000 to $25,000 a year
Custom compliance requirements
$15,000 to $50,000
Enhanced audit trails and reporting
$5,000 to $15,000 a year
Custom data retention configuration
$2,000 to $5,000
HIPAA BAA legal review
$1,000 to $3,000
Custom SSO provider setup
$2,000 to $5,000
SCIM provisioning setup
$1,000 to $3,000
One caution. Gong's help center now offers an EU data center choice to new customers (Gong security FAQ). Ask whether EU hosting is included for you before you accept any residency fee.
⚠️ The operational risks nobody prices
CRM storage load. Vendr's data cites a user report that Gong's Salesforce writes consumed their storage quota at 25MB a day (Vendr). Watch your storage after go-live.
Data flowing back. Getting call data back into the CRM can need extra work, as one reviewer notes below.
Sub-processor tracking. The 5 business day objection window needs someone watching it all year (Gong DPA).
"limitations of getting data back into salesforce" Verified User Gong - G2 Verified Review [5/21/2026]
🔄 What changed: the stack is the risk
Every bolt-on tool adds a DPA, a sub-processor list, a consent setup, and an audit log. The more apps you run, the more security reviews you repeat. Oliv AI's read is simple: RevOps built the stack, and the stack broke RevOps.
🧩 How Oliv AI cuts the review surface
Oliv AI is a revenue orchestration platform that runs agents on one GTM Context Graph, connected to 70+ apps including your CRM. Oliv AI prices its apps at about 30% of incumbent prices, so security and agent budget is not eaten by seats. One platform means one DPA, one sub-processor list, and one audit trail to review.
Q9: How Should RevOps Run a Gong Security Review Without Stalling the Deal? [toc=9. Security Review Checklist]
Run the security review in parallel with the deal, starting 90 days before go-live.
A Gong security review takes about 90 days when it runs in parallel with the commercial deal. RevOps should request the SOC 2 Type II report, ISO certificates, CAIQ, pentest summary, DPA, and sub-processor list in week one (Gong DPA, Gong Trust Center, Gong sub-processors). Security, privacy, and legal then review residency, AI training terms, recording consent, and deletion in that order. Starting 90 days before the target go-live date keeps lagging internal AI policies from stalling the rollout.
⏰ Why 90 days
Rashim Sethi, who sells Oliv AI into enterprise teams, put the cause plainly: "AI has moved so fast, companies' internal IT policies have not developed at that pace." Security teams are not slow on purpose. Many simply have no written policy for AI call bots yet.
So the review has two jobs. Check the vendor, and write the policy you are missing.
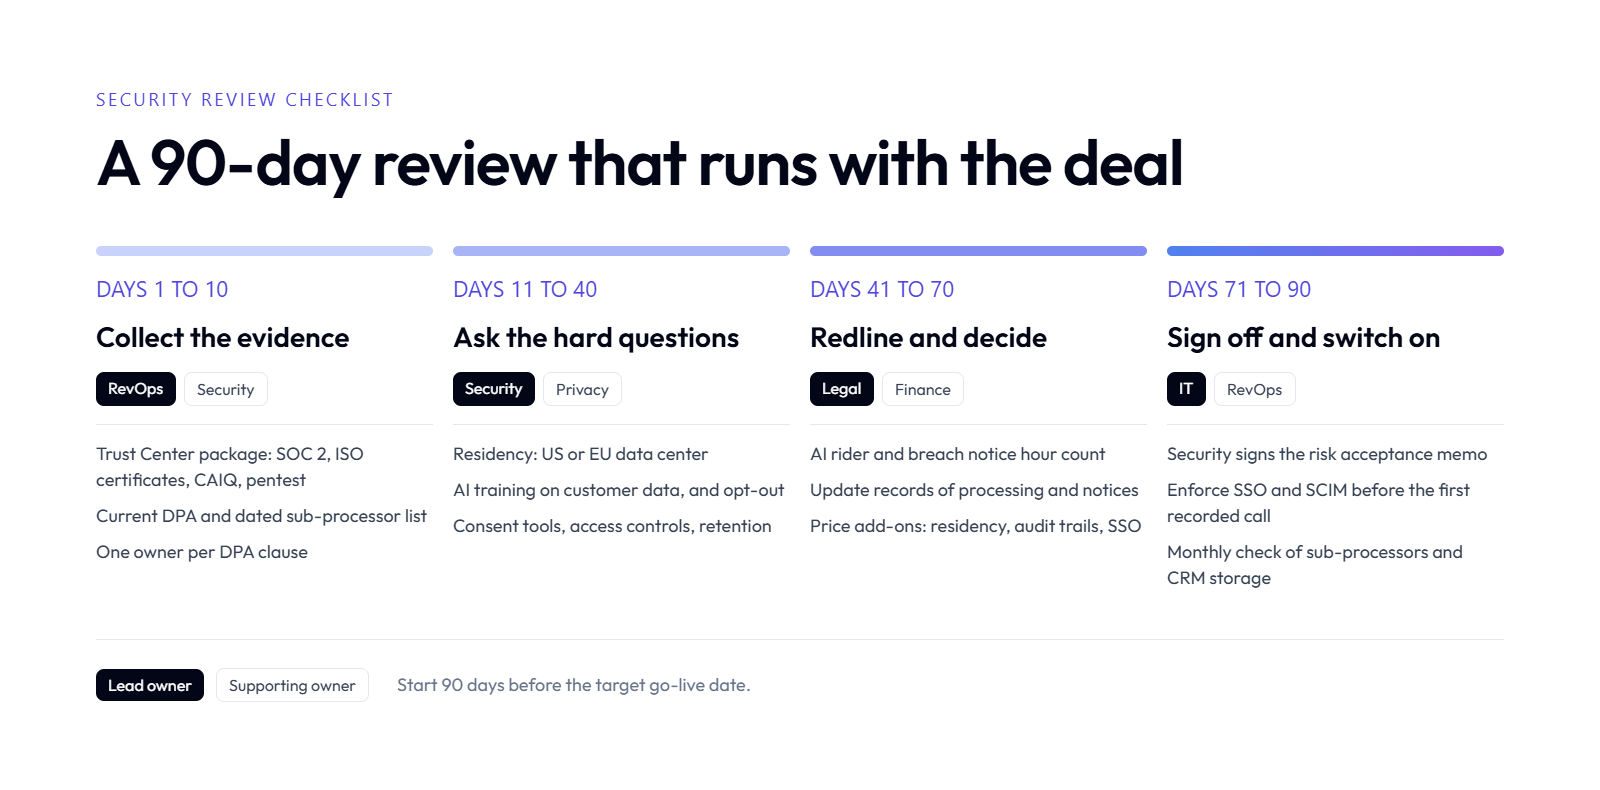
✅ The 90-day checklist
Days 1 to 10: collect the evidence
Request the Trust Center package: SOC 2 Type II, ISO 27001/27017/27018/27701/42001 certificates, CAIQ, and pentest summary (Gong Trust Center).
Download the current DPA and note its "last updated" date (Gong DPA).
Save a copy of the sub-processor list with today's date (Gong sub-processors).
Name one owner per DPA clause, using the table in Q1.
Days 11 to 40: ask the hard questions
Residency: US or EU data center, and is EU hosting included for you (Gong security FAQ)?
Consent: Which consent tools will you configure for each platform and state (Gong Trust Center)?
Access: Confirm SSO, SCIM, permission profiles, and Audit API export (Gong security features).
Retention: Set your retention period and confirm 30-day deletion after the term ends (Gong DPA, Gong security features).
Days 41 to 70: redline and decide
Legal adds the AI rider from Q7 and any breach notice hour count you need.
Privacy updates your records of processing and prospect notices.
Finance prices any residency, audit trail, or SSO add-ons from Q8 (Vendr).
Days 71 to 90: sign off and switch on
Security signs the risk acceptance memo.
IT enforces SSO and SCIM before the first recorded call.
RevOps sets a monthly check of the sub-processor page and CRM storage.
👥 Who owns each phase
Security Review Owners by Phase
Phase
Lead owner
Supporting owner
Evidence
RevOps
Security
Hard questions
Security
Privacy
Redlines
Legal
Finance
Switch on
IT
RevOps
💡 A simpler path
Oliv AI runs the same review with you, and its team supplies trust material at trust.oliv.ai up front. Oliv AI's published timeline is live by week 2, so the security work and the pilot can run side by side.
Q10: How Does an Agent-Based Platform Like Oliv Change the Security Review? [toc=10. Oliv and the Security Review]
Oliv AI is an AI-native revenue intelligence and revenue orchestration platform that runs agents on a single GTM Context Graph on top of your existing CRM. Oliv AI states it is SOC 2 Type II certified, GDPR and CCPA compliant, and encrypts data with AES-256 at rest and TLS 1.2+ in transit. Oliv AI publishes trust material at trust.oliv.ai and offers a full open export policy with no data lock-in. Reviewing one governed agent layer replaces reviewing several separate apps.
📚 How the review used to look
A mid-market revenue team in 2025 often ran a recorder, a forecasting tool, an engagement tool, and a CS platform. Each one meant a DPA, a sub-processor list, a SOC 2 report, and a consent setup. Security reviewed four vendors for one revenue process.
That is the Tool Trap in practice. The stack built to help the team became the thing security had to work around.
❌ What that cost
Every app copied the same call and CRM data into its own store. Every copy needed its own retention rule and deletion path. When a prospect asked to be forgotten, RevOps had to chase four systems.
The review did not get easier with each vendor. It got longer.
⚠️ What changed in 2027
AI agents now act on revenue data, not just display it. They update CRM fields, draft follow-ups, and flag deal risk. The security question moves from "who can see this call" to "what can this agent do, and who approved it".
That needs governance in the platform itself: permissions, approvals, memory controls, and traceability.
🧩 What Oliv AI does about it
Oliv AI builds governance into its agent harness. Here is how that maps to the review.
Oliv AI Security Review Answers
Review question
Oliv AI's answer
Certifications
SOC 2 Type II; GDPR and CCPA compliant
Encryption
AES-256 at rest, TLS 1.2+ in transit
Agent permissions
Olivia asks before acting; Oliver acts without asking for RevOps-owned rules
Audit
Harness includes audit and security, monitoring, and logging
Data exit
Full open export, no lock-in
Capture consent
Consent-first in-person capture through the Plaud partnership
Oliv AI also runs on top of Gong if you are mid-contract. You can review Oliv AI now and decide at renewal, with no overlap cost.
🗣️ What customers say
"It doesn't just record meetings; it automatically captures key insights, updates systems of record, identifies next steps, and helps keep teams aligned." Verified User Oliv AI G2 - Verified Review [6/23/2026]
"The only downside is that the platform can be a bit glitchy at times, but the support team is always quick to address and resolve any bugs." Verified User Oliv AI G2 - Verified Review [7/2/2026]
Oliv AI is not the right fit for everyone. If you only want call recording, or you run a B2C support team, a simpler recorder will do. If your security team is tired of reviewing the same data in four places, tell us what your review looks like. We will walk through it with you in seven minutes, no pitch.
A RevOps manager at Oliv AI was looking at website analytics one morning and noticed something odd. An enterprise prospect's team had skipped the pricing page entirely. They went straight to the footer, opened the privacy policy, and read it closely before they ever booked a call. That is how security review starts now. It starts before the first meeting, and it starts with the paperwork.
If you are reviewing Gong, here is the short answer. Gong's Data Processing Addendum (DPA) and certifications are a solid enterprise baseline. The real review work sits in five places: recording consent, AI data use, data residency, sub-processor tracking, and add-on cost. Most of that risk belongs to you, because under GDPR you are the controller. This guide walks through the September 2026 DPA in plain language and shows you what to check, who owns it, and how to finish the review without stalling the deal for a quarter.
Q1: What Is the Gong DPA and What Does It Actually Commit Gong To? [toc=1. What the Gong DPA Says]
Each time window in the Gong DPA needs a named owner on your side.
The Gong DPA is the Data Processing Addendum that forms part of Gong's terms and conditions. It names the customer as the controller and Gong as the processor of personal data in calls, emails, and CRM records. The version published on gong.io is marked "last updated September 2026" (Gong DPA). It sets transfer terms for the EU, UK, and Switzerland, a 5 business day window to object to new sub-processors, audit rights once a year on 45 days' notice, breach notice "without undue delay", and deletion of customer data 30 days after the contract ends (Gong DPA).
📄 Who does what under the DPA
A controller decides why and how personal data is used. A processor handles that data only on the controller's instructions. Under section 2.1 of the DPA, your company is the controller (the "business" under the California Consumer Privacy Act, or CCPA) and Gong is the processor (the "service provider") (Gong DPA).
There is one exception worth flagging. For Gong Enrich, the DPA's Schedule 2 makes Gong an independent controller of enrichment data (Gong DPA). If your team uses Enrich, that data sits under Gong's own privacy decisions, not only yours.
⚠️ The sensitive data line
Section 2.3 says the services "are not intended for the Processing of Sensitive Data" (Gong DPA). That is a statement of intent, not a technical block. Health details, financial account numbers, or union membership can still come up on a sales call. Your team carries the duty to keep that data out or to handle it lawfully under section 2.4 (Gong DPA).
⏰ The clause-to-action table
These are the time windows in the DPA that need a named owner on your side.
Gong DPA Clauses and Owners
DPA clause
What it says
Who should own it
Sub-processors (§5.2)
You may object within 5 business days of notice of a new sub-processor
Gong notifies "without undue delay"; details may arrive in phases
Incident response owner
Audit (§9.2)
Once a year, 45 days' written notice, except after a breach
Security lead, calendar the request
Deletion (§10)
All customer data deleted 30 days after termination or expiry; backups isolated
RevOps, plan exports before the end date
Changes (§14)
Either party may request changes on 45 days' notice; 30 days to agree
Legal
💡 What this means on Monday
The DPA gives you no hour count for breach notice. If your own policy needs one, such as 72 hours, ask for it in your order form. The 5 business day objection window is short, so the sub-processor page needs an owner, not a quarterly glance.
Oliv AI sees the same pattern in its own enterprise security reviews. The DPA is rarely what blocks a deal. The missing owner for each clause is. Oliv AI publishes its own trust material at trust.oliv.ai, so you can run the same clause-to-owner exercise on us side by side.
Q2: How Does Gong Handle GDPR, CCPA and International Data Transfers? [toc=2. GDPR, CCPA and Transfers]
Gong handles GDPR and CCPA through its DPA, which assigns the customer the controller role and Gong the processor role (Gong DPA). For data leaving the European Economic Area, the DPA uses the EU Standard Contractual Clauses (SCCs) under Decision 2021/914, Modules One to Four, governed by Irish law (Gong DPA). It adds the UK Addendum issued by the Information Commissioner's Office and a Swiss schedule under the Federal Act on Data Protection (FADP) (Gong DPA). Gong also states it is certified under the EU-U.S. Data Privacy Framework (Gong security FAQ).
🌍 The transfer stack, in plain words
Standard Contractual Clauses are pre-approved contract terms from the European Commission. They let personal data move to a country without an EU "adequacy" decision. Here is how Gong's stack lines up.
Gong Data Transfer Mechanisms by Region
Region
Mechanism in the Gong DPA
Source
EU and EEA
EU SCCs, Decision 2021/914, Modules One to Four, Irish law and courts
Part 4 of the schedule adds extra safeguards, including encryption in transit and at rest and rules for government access requests (Gong DPA).
⚖️ CCPA terms
Under section 2.5, Gong may not sell or share personal information as those terms are defined in the CCPA (Gong DPA). Gong processes data only on your documented instructions, and anonymization is listed as a permitted instruction under section 2.4 (Gong DPA).
✅ What stays with you as controller
Paper compliance on Gong's side does not move your duties. You still own these tasks.
Lawful basis. Decide and record why you process call data, such as legitimate interest or consent.
Data subject requests. Respond when a prospect asks to see or delete their data. Gong's FAQ points to API and in-app tools for the right to be forgotten (Gong security FAQ).
Notices. Tell prospects and employees that calls are recorded and analyzed.
Records of processing. List Gong and its sub-processors in your own records.
I have watched a privacy lead approve a vendor on the strength of its DPF certificate, then realize nobody owned deletion requests. The certificate was fine. The workflow was missing.
Oliv AI states that it is GDPR and CCPA compliant and offers a full open export policy with no data lock-in. That makes access and deletion requests simpler to answer, because the data is not trapped in one app's format.
Q3: Which Security Certifications Does Gong Hold in 2027, and How Do You Verify Them? [toc=3. Gong Security Certifications]
Gong's help center lists a SOC 2 Type II report, ISO/IEC 27001, 27017, 27018, and 27701 certificates, and a listing in the Cloud Security Alliance (CSA) STAR Registry (Gong security FAQ, Gong security features). Gong also lists ISO 42001:2023, the AI management system standard, which it says it earned in June 2025 (Gong security features, Gong responsible AI). Reports and certificates are available through the Gong Trust Center, where you request access before review (Gong Trust Center).
📋 What each certificate covers
Each certificate answers a different question. None of them answers all of them.
What Each Gong Certification Proves
Certification
What it shows
What it does not prove
SOC 2 Type II
An auditor tested security controls over a period of time
That your tenant settings are correct
ISO 27001
A managed information security system exists and is audited
Control depth for every product
ISO 27017 / 27018
Cloud security controls and protection of personal data in the cloud
Your consent workflow
ISO 27701
A privacy information management system on top of 27001
Lawful basis for your processing
ISO 42001
An audited AI governance program
Whether your calls train any model
CSA STAR
A published cloud security self-assessment or audit
Ongoing compliance between audits
🔍 How to verify, step by step
Request the package. Ask for the SOC 2 Type II report, ISO certificates, the CAIQ (the Cloud Security Alliance's standard security questionnaire), and the pentest summary through the Trust Center (Gong Trust Center).
Check the audit window. A SOC 2 Type II report covers a set period. Note the end date and ask for a bridge letter if it is older than six months.
Check scope. Confirm the products you buy, such as Engage or Forecast, sit inside the certified scope.
Check certificate dates. One 2025 third-party review said Gong's ISO 27001 certificate expired in October 2025. Gong's own pages now list ISO/IEC 27001:2022 (Gong Trust Center). Confirm the current certificate in the Trust Center rather than trusting any blog, including this one.
Log exceptions. Read the auditor's exceptions section, not only the opinion letter.
🧭 My honest read
Gong is a market leader, and it holds the certifications a market leader should hold. I would not build a security case against Gong on missing paperwork. The questions that matter sit in consent, AI data use, and residency, which the next sections cover.
Oliv AI is SOC 2 Type II certified and publishes its trust material at trust.oliv.ai. Ask Oliv AI for the same package you ask Gong for, and compare the audit windows and scope line by line.
Q4: Where Is Your Sales Data Stored and How Is It Protected? [toc=4. Data Storage and Protection]
Where Gong stores data and where it can be processed are two different questions.
Gong is hosted on Amazon Web Services (AWS). Gong's help center says new customers can choose US or EU data centers, with the US as the default (Gong security FAQ). Data is encrypted in transit with at least TLS 1.2 and at rest with AES-256, and customers can bring their own encryption key (BYOK) (Gong security features). Gong's offices in the US, Israel, and Ireland may process data, and its sub-processors sit in the US, UK, and EMEA (Gong security FAQ). Customer data is deleted within 30 days of contract end (Gong DPA, Gong security FAQ).
🗺️ How it used to work
For years, the standard answer on Gong storage was "it lives in the US." Many 2025 reviews, including the earlier version of this guide, said all customer data was stored in the United States. EU security teams treated that as a blocker or paid for workarounds.
That picture is now out of date. Gong's FAQ confirms the US and EU choice for new customers (Gong security FAQ). If you signed before that option existed, ask your account team in writing whether migration is possible and what it costs.
🔐 Storage is not the same as processing
Here is the part that catches teams out. Where data rests is one question. Where it can be accessed or processed is another.
Storage: US by default or EU on request, on AWS (Gong security FAQ).
Processing: Gong offices in the US, Israel, and Ireland (Gong security FAQ).
Retention: set by you and changeable at any time, per Gong's security page (Gong security features).
Deletion: 30 days after the contract ends, with backups isolated rather than wiped at once (Gong DPA).
⚠️ What changed with AI
Conversation intelligence used to mean a recording, a transcript, and a dashboard. Now each call feeds AI summaries, trackers, and agents. Every new AI feature can mean another processing step, and sometimes another sub-processor. The map of where your data travels grows each quarter, even if the storage region never changes.
Customer reviews show the operational side of this. One reviewer noted the cost of leaving.
"if you stop working with thew tool you lose the data" Verified User Gong - G2 Verified Review [3/19/2026]
"I cannot download all the data myself unless we upgrade the plan" Verified User Gong - G2 Verified Review [10/3/2025]
🧩 How Oliv AI approaches data flow
Oliv AI is an AI-native revenue intelligence platform that keeps account and deal context in one governed layer, the GTM Context Graph, instead of copying it across several bolt-on apps. Oliv AI encrypts data with AES-256 at rest and TLS 1.2+ in transit, and its open export policy means you keep your data when you leave. Fewer copies in fewer apps means a shorter data map for your security team to approve.
Q5: Which Access Controls and Audit Features Matter for an Enterprise Rollout? [toc=5. Access Controls and Audit]
Gong supports single sign-on (SSO) through SAML 2.0, OAuth 2.0, and OpenID Connect, plus SCIM provisioning for automatic user setup and removal (Gong security features). It ships four built-in roles (Collaborator, Standard user, Business administrator, and Technical administrator) and granular permission profiles by person, team, or group (Gong security features). The Gong Audit API exports activity logs in JSON, covering platform use and Gong staff access to customer data (Gong security features). Gong runs third-party penetration tests, a bug bounty, and a Vulnerability Disclosure Program at vdp.gong.io (Gong security features).
🧑💼 How access control used to work
The classic rollout went like this. IT connected SSO, RevOps created users by hand, and every manager got broad access "for now". Six months later, nobody could say who could hear which calls. A departed rep's account was still active because nobody owned offboarding.
That was the real risk in conversation intelligence. The controls existed. They were simply switched on late, or not at all.
✅ What to switch on in week one
Use this list before the first call is recorded.
SSO, enforced. Turn off password login once SSO works.
SCIM provisioning. SCIM (System for Cross-domain Identity Management) creates and removes users from your identity provider, so leavers lose access the same day.
Permission profiles. Restrict call access by team. Sales managers rarely need every CS call.
Audit API export. Send logs to your security tool weekly, not only after an incident.
BYOK, if policy requires it. Bring your own key gives you control over encryption keys (Gong security features).
⚠️ What changed: agents need permissions too
Here is the shift most security reviews miss. In 2027, people are not the only actors touching call data. AI agents now read transcripts, draft emails, and update CRM fields. A role model built for humans does not tell you what an agent may do without asking.
Ask every vendor, Gong included, a direct question. Which AI features can write to our CRM or send messages on their own, and where is that logged?
🛡️ How Oliv AI splits agent permissions
Oliv AI builds the permission model into its two super-agents. Olivia, Oliv AI's Chief of AI Staff, works on an "Ask before acting" model for AEs, BDRs, AMs, and CS managers. Oliver, the Chief AI GTM Engineer, works on "Act without asking" for RevOps and sales leaders who own the playbook.
Oliv AI's agent harness lists guardrails, audit and security, and monitoring and logging as core parts. That gives your security team one place to see what an agent did and why. We designed it that way because a human role chart cannot govern software that acts.
"The Analyst agent allows me to understand everything I need with just one click, eliminating the long wait time I used to have with RevOps to get answers." Verified User Oliv AI G2 - Verified Review [6/17/2026]
Q6: Who Owns Call Recording Consent, and What Changes in Two-Party Consent States? [toc=6. Recording Consent]
Gong provides consent tools, but the customer stays accountable for recording consent.
The customer owns recording consent. Gong provides tools that help, including consent links, a personalized consent page, and audio prompt or Zoom-based consent options (Gong Trust Center). Gong's FAQ says sales calls can be recorded "in compliance with the right workflows", which leaves configuring those workflows to the customer (Gong security FAQ). In two-party (all-party) consent states such as California, every participant must agree. California's Invasion of Privacy Act (CIPA) allows $5,000 in statutory damages per violation (Holland & Knight).
📞 How consent used to work
For years, the standard answer was a line in the calendar invite and a "this call may be recorded" notice. Legal signed off once. Nobody checked whether the prompt fired on every platform, or for every guest who joined late.
That worked because lawsuits targeted the company on the call, and most claims went nowhere.
❌ What that cost
Now the targets have changed. Holland & Knight reported in July 2025 that class actions have begun to target AI call vendors, not only the businesses using them (Holland & Knight). Suits against Cresta and ConverseNow claim that AI tools captured and analyzed calls without valid consent (Holland & Knight, Fisher Phillips).
In August 2025, a federal court in Northern California denied ConverseNow's motion to dismiss a CIPA class action (Fisher Phillips). Commentators also question whether generic "may be monitored for quality" notices are enough once AI analysis is involved (Fisher Phillips). To be fair, results differ. In February 2025, a court dismissed a CIPA claim against Talkdesk because the calls were not private enough to support standing (Fisher Phillips).
I am not a lawyer, and this is not legal advice. Talk to counsel about the states and countries you sell into.
⏰ What changed with AI capture
Recording is no longer one Zoom call. Revenue teams now capture mobile calls, in-person meetings, and chat. Each new channel needs its own consent moment, or the risk travels with the data.
🎙️ How Oliv AI handles consent-first capture
Oliv AI captures context across five ways revenue teams communicate, including in-person meetings. For physical meetings, Oliv AI's partnership with Plaud brings what Oliv AI calls ambient, consent-first capture. The point is simple. Consent should be designed into the capture step, not added as a footer later.
Q7: How Does Gong Use Your Call Data for AI, and What Does the EU AI Act Change? [toc=7. AI Data Use and the EU AI Act]
Gong's DPA does not address whether customer data trains AI models (Gong DPA). Gong holds ISO 42001, the AI management system standard, earned in June 2025 (Gong responsible AI). Gong points customers to the AI section of its Trust Center for AI data practices (Gong security features, Gong Trust Center). The independent VerifyWise AI Trust Index grades Gong "B" and notes that public policy does not state whether inputs are kept out of model training (VerifyWise). Under the EU AI Act, workplace emotion recognition has been prohibited since February 2, 2025 (EU AI Act).
🤖 How AI review used to work
Two years ago, the AI question in a security review was one checkbox. Does the vendor use AI? Yes. Next question.
That was fine when AI meant a transcript and a keyword tracker. It is not fine when AI summarizes every deal, scores reps, and drafts customer emails.
❌ Where the gap is now
ISO 42001 proves that Gong runs an audited AI governance program (Gong responsible AI). It does not tell you whether your calls train a shared model. Even Gong's own AI governance post lists "Can I prevent certain data from being used in AI prompts and training?" as a question customers should ask (Gong AI governance). That is a good question. Ask it in writing.
Here is the AI rider language I would request in the order form.
Customer data is not used to train models shared with other customers.
Customer may opt out of AI features by workspace or team.
Gong lists every AI sub-processor and its region.
Gong gives notice before a new AI feature processes customer data.
⚖️ What the EU AI Act changes
The EU AI Act is Regulation (EU) 2024/1689 (EU AI Act). Article 5(1)(f) bans AI that infers the emotions of people at work, except for medical or safety reasons. That ban has applied since February 2, 2025 (EU AI Act). Article 50 transparency duties, which cover telling people about emotion recognition, apply from August 2, 2026 (EU AI Act).
For revenue teams, the practical question is narrow. Does any feature infer a rep's emotion from their voice? If your reps are in the EU, switch that feature off or get a written legal view. Text-only sentiment on emails is generally treated differently, but confirm it with counsel.
🧠 How Oliv AI approaches AI data use
Oliv AI runs more than 100 fine-tuned small language models (SLMs), each trained for one revenue question, such as pains, decision makers, or budget. Oliv AI reports under 1% hallucinations in production for this narrow design. Narrow models do one job, which makes "what does this model see and why" an easier question to answer in review.
"I love how Oliv AI goes beyond simple call transcription to actually interpret and extract actionable insights from every interaction." Verified User Oliv AI G2 - Verified Review [7/8/2026]
Q8: What Hidden Costs and Operational Risks Come With a Gong Security Setup? [toc=8. Hidden Costs and Risks]
Gong does not publish list prices, so security costs show up during negotiation. Vendr's Gong pricing data estimates dedicated regional hosting at $10,000 to $25,000 a year, custom compliance requirements at $15,000 to $50,000, and enhanced audit trails at $5,000 to $15,000 a year (Vendr). The same data puts custom SSO setup at $2,000 to $5,000 and SCIM setup at $1,000 to $3,000 (Vendr). Operational risks include CRM storage load from synced call data and the overhead of tracking sub-processor changes.
💸 How the bill used to look
A typical Gong budget covered seats and a platform fee. Security lived in a separate column that nobody priced. Then the EU team asked for regional hosting, legal asked for longer audit logs, and IT asked for custom SSO.
Each request was small. Together, they changed the deal.
💰 The add-on ranges to budget for
These are third-party estimates, not Gong list prices. Treat them as a starting point for negotiation (Vendr).
Estimated Gong Security Add-On Costs
Item
Estimated cost
Dedicated regional data residency
$10,000 to $25,000 a year
Custom compliance requirements
$15,000 to $50,000
Enhanced audit trails and reporting
$5,000 to $15,000 a year
Custom data retention configuration
$2,000 to $5,000
HIPAA BAA legal review
$1,000 to $3,000
Custom SSO provider setup
$2,000 to $5,000
SCIM provisioning setup
$1,000 to $3,000
One caution. Gong's help center now offers an EU data center choice to new customers (Gong security FAQ). Ask whether EU hosting is included for you before you accept any residency fee.
⚠️ The operational risks nobody prices
CRM storage load. Vendr's data cites a user report that Gong's Salesforce writes consumed their storage quota at 25MB a day (Vendr). Watch your storage after go-live.
Data flowing back. Getting call data back into the CRM can need extra work, as one reviewer notes below.
Sub-processor tracking. The 5 business day objection window needs someone watching it all year (Gong DPA).
"limitations of getting data back into salesforce" Verified User Gong - G2 Verified Review [5/21/2026]
🔄 What changed: the stack is the risk
Every bolt-on tool adds a DPA, a sub-processor list, a consent setup, and an audit log. The more apps you run, the more security reviews you repeat. Oliv AI's read is simple: RevOps built the stack, and the stack broke RevOps.
🧩 How Oliv AI cuts the review surface
Oliv AI is a revenue orchestration platform that runs agents on one GTM Context Graph, connected to 70+ apps including your CRM. Oliv AI prices its apps at about 30% of incumbent prices, so security and agent budget is not eaten by seats. One platform means one DPA, one sub-processor list, and one audit trail to review.
Q9: How Should RevOps Run a Gong Security Review Without Stalling the Deal? [toc=9. Security Review Checklist]
Run the security review in parallel with the deal, starting 90 days before go-live.
A Gong security review takes about 90 days when it runs in parallel with the commercial deal. RevOps should request the SOC 2 Type II report, ISO certificates, CAIQ, pentest summary, DPA, and sub-processor list in week one (Gong DPA, Gong Trust Center, Gong sub-processors). Security, privacy, and legal then review residency, AI training terms, recording consent, and deletion in that order. Starting 90 days before the target go-live date keeps lagging internal AI policies from stalling the rollout.
⏰ Why 90 days
Rashim Sethi, who sells Oliv AI into enterprise teams, put the cause plainly: "AI has moved so fast, companies' internal IT policies have not developed at that pace." Security teams are not slow on purpose. Many simply have no written policy for AI call bots yet.
So the review has two jobs. Check the vendor, and write the policy you are missing.
✅ The 90-day checklist
Days 1 to 10: collect the evidence
Request the Trust Center package: SOC 2 Type II, ISO 27001/27017/27018/27701/42001 certificates, CAIQ, and pentest summary (Gong Trust Center).
Download the current DPA and note its "last updated" date (Gong DPA).
Save a copy of the sub-processor list with today's date (Gong sub-processors).
Name one owner per DPA clause, using the table in Q1.
Days 11 to 40: ask the hard questions
Residency: US or EU data center, and is EU hosting included for you (Gong security FAQ)?
Consent: Which consent tools will you configure for each platform and state (Gong Trust Center)?
Access: Confirm SSO, SCIM, permission profiles, and Audit API export (Gong security features).
Retention: Set your retention period and confirm 30-day deletion after the term ends (Gong DPA, Gong security features).
Days 41 to 70: redline and decide
Legal adds the AI rider from Q7 and any breach notice hour count you need.
Privacy updates your records of processing and prospect notices.
Finance prices any residency, audit trail, or SSO add-ons from Q8 (Vendr).
Days 71 to 90: sign off and switch on
Security signs the risk acceptance memo.
IT enforces SSO and SCIM before the first recorded call.
RevOps sets a monthly check of the sub-processor page and CRM storage.
👥 Who owns each phase
Security Review Owners by Phase
Phase
Lead owner
Supporting owner
Evidence
RevOps
Security
Hard questions
Security
Privacy
Redlines
Legal
Finance
Switch on
IT
RevOps
💡 A simpler path
Oliv AI runs the same review with you, and its team supplies trust material at trust.oliv.ai up front. Oliv AI's published timeline is live by week 2, so the security work and the pilot can run side by side.
Q10: How Does an Agent-Based Platform Like Oliv Change the Security Review? [toc=10. Oliv and the Security Review]
Oliv AI is an AI-native revenue intelligence and revenue orchestration platform that runs agents on a single GTM Context Graph on top of your existing CRM. Oliv AI states it is SOC 2 Type II certified, GDPR and CCPA compliant, and encrypts data with AES-256 at rest and TLS 1.2+ in transit. Oliv AI publishes trust material at trust.oliv.ai and offers a full open export policy with no data lock-in. Reviewing one governed agent layer replaces reviewing several separate apps.
📚 How the review used to look
A mid-market revenue team in 2025 often ran a recorder, a forecasting tool, an engagement tool, and a CS platform. Each one meant a DPA, a sub-processor list, a SOC 2 report, and a consent setup. Security reviewed four vendors for one revenue process.
That is the Tool Trap in practice. The stack built to help the team became the thing security had to work around.
❌ What that cost
Every app copied the same call and CRM data into its own store. Every copy needed its own retention rule and deletion path. When a prospect asked to be forgotten, RevOps had to chase four systems.
The review did not get easier with each vendor. It got longer.
⚠️ What changed in 2027
AI agents now act on revenue data, not just display it. They update CRM fields, draft follow-ups, and flag deal risk. The security question moves from "who can see this call" to "what can this agent do, and who approved it".
That needs governance in the platform itself: permissions, approvals, memory controls, and traceability.
🧩 What Oliv AI does about it
Oliv AI builds governance into its agent harness. Here is how that maps to the review.
Oliv AI Security Review Answers
Review question
Oliv AI's answer
Certifications
SOC 2 Type II; GDPR and CCPA compliant
Encryption
AES-256 at rest, TLS 1.2+ in transit
Agent permissions
Olivia asks before acting; Oliver acts without asking for RevOps-owned rules
Audit
Harness includes audit and security, monitoring, and logging
Data exit
Full open export, no lock-in
Capture consent
Consent-first in-person capture through the Plaud partnership
Oliv AI also runs on top of Gong if you are mid-contract. You can review Oliv AI now and decide at renewal, with no overlap cost.
🗣️ What customers say
"It doesn't just record meetings; it automatically captures key insights, updates systems of record, identifies next steps, and helps keep teams aligned." Verified User Oliv AI G2 - Verified Review [6/23/2026]
"The only downside is that the platform can be a bit glitchy at times, but the support team is always quick to address and resolve any bugs." Verified User Oliv AI G2 - Verified Review [7/2/2026]
Oliv AI is not the right fit for everyone. If you only want call recording, or you run a B2C support team, a simpler recorder will do. If your security team is tired of reviewing the same data in four places, tell us what your review looks like. We will walk through it with you in seven minutes, no pitch.
A RevOps manager at Oliv AI was looking at website analytics one morning and noticed something odd. An enterprise prospect's team had skipped the pricing page entirely. They went straight to the footer, opened the privacy policy, and read it closely before they ever booked a call. That is how security review starts now. It starts before the first meeting, and it starts with the paperwork.
If you are reviewing Gong, here is the short answer. Gong's Data Processing Addendum (DPA) and certifications are a solid enterprise baseline. The real review work sits in five places: recording consent, AI data use, data residency, sub-processor tracking, and add-on cost. Most of that risk belongs to you, because under GDPR you are the controller. This guide walks through the September 2026 DPA in plain language and shows you what to check, who owns it, and how to finish the review without stalling the deal for a quarter.
Q1: What Is the Gong DPA and What Does It Actually Commit Gong To? [toc=1. What the Gong DPA Says]
Each time window in the Gong DPA needs a named owner on your side.
The Gong DPA is the Data Processing Addendum that forms part of Gong's terms and conditions. It names the customer as the controller and Gong as the processor of personal data in calls, emails, and CRM records. The version published on gong.io is marked "last updated September 2026" (Gong DPA). It sets transfer terms for the EU, UK, and Switzerland, a 5 business day window to object to new sub-processors, audit rights once a year on 45 days' notice, breach notice "without undue delay", and deletion of customer data 30 days after the contract ends (Gong DPA).
📄 Who does what under the DPA
A controller decides why and how personal data is used. A processor handles that data only on the controller's instructions. Under section 2.1 of the DPA, your company is the controller (the "business" under the California Consumer Privacy Act, or CCPA) and Gong is the processor (the "service provider") (Gong DPA).
There is one exception worth flagging. For Gong Enrich, the DPA's Schedule 2 makes Gong an independent controller of enrichment data (Gong DPA). If your team uses Enrich, that data sits under Gong's own privacy decisions, not only yours.
⚠️ The sensitive data line
Section 2.3 says the services "are not intended for the Processing of Sensitive Data" (Gong DPA). That is a statement of intent, not a technical block. Health details, financial account numbers, or union membership can still come up on a sales call. Your team carries the duty to keep that data out or to handle it lawfully under section 2.4 (Gong DPA).
⏰ The clause-to-action table
These are the time windows in the DPA that need a named owner on your side.
Gong DPA Clauses and Owners
DPA clause
What it says
Who should own it
Sub-processors (§5.2)
You may object within 5 business days of notice of a new sub-processor
Gong notifies "without undue delay"; details may arrive in phases
Incident response owner
Audit (§9.2)
Once a year, 45 days' written notice, except after a breach
Security lead, calendar the request
Deletion (§10)
All customer data deleted 30 days after termination or expiry; backups isolated
RevOps, plan exports before the end date
Changes (§14)
Either party may request changes on 45 days' notice; 30 days to agree
Legal
💡 What this means on Monday
The DPA gives you no hour count for breach notice. If your own policy needs one, such as 72 hours, ask for it in your order form. The 5 business day objection window is short, so the sub-processor page needs an owner, not a quarterly glance.
Oliv AI sees the same pattern in its own enterprise security reviews. The DPA is rarely what blocks a deal. The missing owner for each clause is. Oliv AI publishes its own trust material at trust.oliv.ai, so you can run the same clause-to-owner exercise on us side by side.
Q2: How Does Gong Handle GDPR, CCPA and International Data Transfers? [toc=2. GDPR, CCPA and Transfers]
Gong handles GDPR and CCPA through its DPA, which assigns the customer the controller role and Gong the processor role (Gong DPA). For data leaving the European Economic Area, the DPA uses the EU Standard Contractual Clauses (SCCs) under Decision 2021/914, Modules One to Four, governed by Irish law (Gong DPA). It adds the UK Addendum issued by the Information Commissioner's Office and a Swiss schedule under the Federal Act on Data Protection (FADP) (Gong DPA). Gong also states it is certified under the EU-U.S. Data Privacy Framework (Gong security FAQ).
🌍 The transfer stack, in plain words
Standard Contractual Clauses are pre-approved contract terms from the European Commission. They let personal data move to a country without an EU "adequacy" decision. Here is how Gong's stack lines up.
Gong Data Transfer Mechanisms by Region
Region
Mechanism in the Gong DPA
Source
EU and EEA
EU SCCs, Decision 2021/914, Modules One to Four, Irish law and courts
Part 4 of the schedule adds extra safeguards, including encryption in transit and at rest and rules for government access requests (Gong DPA).
⚖️ CCPA terms
Under section 2.5, Gong may not sell or share personal information as those terms are defined in the CCPA (Gong DPA). Gong processes data only on your documented instructions, and anonymization is listed as a permitted instruction under section 2.4 (Gong DPA).
✅ What stays with you as controller
Paper compliance on Gong's side does not move your duties. You still own these tasks.
Lawful basis. Decide and record why you process call data, such as legitimate interest or consent.
Data subject requests. Respond when a prospect asks to see or delete their data. Gong's FAQ points to API and in-app tools for the right to be forgotten (Gong security FAQ).
Notices. Tell prospects and employees that calls are recorded and analyzed.
Records of processing. List Gong and its sub-processors in your own records.
I have watched a privacy lead approve a vendor on the strength of its DPF certificate, then realize nobody owned deletion requests. The certificate was fine. The workflow was missing.
Oliv AI states that it is GDPR and CCPA compliant and offers a full open export policy with no data lock-in. That makes access and deletion requests simpler to answer, because the data is not trapped in one app's format.
Q3: Which Security Certifications Does Gong Hold in 2027, and How Do You Verify Them? [toc=3. Gong Security Certifications]
Gong's help center lists a SOC 2 Type II report, ISO/IEC 27001, 27017, 27018, and 27701 certificates, and a listing in the Cloud Security Alliance (CSA) STAR Registry (Gong security FAQ, Gong security features). Gong also lists ISO 42001:2023, the AI management system standard, which it says it earned in June 2025 (Gong security features, Gong responsible AI). Reports and certificates are available through the Gong Trust Center, where you request access before review (Gong Trust Center).
📋 What each certificate covers
Each certificate answers a different question. None of them answers all of them.
What Each Gong Certification Proves
Certification
What it shows
What it does not prove
SOC 2 Type II
An auditor tested security controls over a period of time
That your tenant settings are correct
ISO 27001
A managed information security system exists and is audited
Control depth for every product
ISO 27017 / 27018
Cloud security controls and protection of personal data in the cloud
Your consent workflow
ISO 27701
A privacy information management system on top of 27001
Lawful basis for your processing
ISO 42001
An audited AI governance program
Whether your calls train any model
CSA STAR
A published cloud security self-assessment or audit
Ongoing compliance between audits
🔍 How to verify, step by step
Request the package. Ask for the SOC 2 Type II report, ISO certificates, the CAIQ (the Cloud Security Alliance's standard security questionnaire), and the pentest summary through the Trust Center (Gong Trust Center).
Check the audit window. A SOC 2 Type II report covers a set period. Note the end date and ask for a bridge letter if it is older than six months.
Check scope. Confirm the products you buy, such as Engage or Forecast, sit inside the certified scope.
Check certificate dates. One 2025 third-party review said Gong's ISO 27001 certificate expired in October 2025. Gong's own pages now list ISO/IEC 27001:2022 (Gong Trust Center). Confirm the current certificate in the Trust Center rather than trusting any blog, including this one.
Log exceptions. Read the auditor's exceptions section, not only the opinion letter.
🧭 My honest read
Gong is a market leader, and it holds the certifications a market leader should hold. I would not build a security case against Gong on missing paperwork. The questions that matter sit in consent, AI data use, and residency, which the next sections cover.
Oliv AI is SOC 2 Type II certified and publishes its trust material at trust.oliv.ai. Ask Oliv AI for the same package you ask Gong for, and compare the audit windows and scope line by line.
Q4: Where Is Your Sales Data Stored and How Is It Protected? [toc=4. Data Storage and Protection]
Where Gong stores data and where it can be processed are two different questions.
Gong is hosted on Amazon Web Services (AWS). Gong's help center says new customers can choose US or EU data centers, with the US as the default (Gong security FAQ). Data is encrypted in transit with at least TLS 1.2 and at rest with AES-256, and customers can bring their own encryption key (BYOK) (Gong security features). Gong's offices in the US, Israel, and Ireland may process data, and its sub-processors sit in the US, UK, and EMEA (Gong security FAQ). Customer data is deleted within 30 days of contract end (Gong DPA, Gong security FAQ).
🗺️ How it used to work
For years, the standard answer on Gong storage was "it lives in the US." Many 2025 reviews, including the earlier version of this guide, said all customer data was stored in the United States. EU security teams treated that as a blocker or paid for workarounds.
That picture is now out of date. Gong's FAQ confirms the US and EU choice for new customers (Gong security FAQ). If you signed before that option existed, ask your account team in writing whether migration is possible and what it costs.
🔐 Storage is not the same as processing
Here is the part that catches teams out. Where data rests is one question. Where it can be accessed or processed is another.
Storage: US by default or EU on request, on AWS (Gong security FAQ).
Processing: Gong offices in the US, Israel, and Ireland (Gong security FAQ).
Retention: set by you and changeable at any time, per Gong's security page (Gong security features).
Deletion: 30 days after the contract ends, with backups isolated rather than wiped at once (Gong DPA).
⚠️ What changed with AI
Conversation intelligence used to mean a recording, a transcript, and a dashboard. Now each call feeds AI summaries, trackers, and agents. Every new AI feature can mean another processing step, and sometimes another sub-processor. The map of where your data travels grows each quarter, even if the storage region never changes.
Customer reviews show the operational side of this. One reviewer noted the cost of leaving.
"if you stop working with thew tool you lose the data" Verified User Gong - G2 Verified Review [3/19/2026]
"I cannot download all the data myself unless we upgrade the plan" Verified User Gong - G2 Verified Review [10/3/2025]
🧩 How Oliv AI approaches data flow
Oliv AI is an AI-native revenue intelligence platform that keeps account and deal context in one governed layer, the GTM Context Graph, instead of copying it across several bolt-on apps. Oliv AI encrypts data with AES-256 at rest and TLS 1.2+ in transit, and its open export policy means you keep your data when you leave. Fewer copies in fewer apps means a shorter data map for your security team to approve.
Q5: Which Access Controls and Audit Features Matter for an Enterprise Rollout? [toc=5. Access Controls and Audit]
Gong supports single sign-on (SSO) through SAML 2.0, OAuth 2.0, and OpenID Connect, plus SCIM provisioning for automatic user setup and removal (Gong security features). It ships four built-in roles (Collaborator, Standard user, Business administrator, and Technical administrator) and granular permission profiles by person, team, or group (Gong security features). The Gong Audit API exports activity logs in JSON, covering platform use and Gong staff access to customer data (Gong security features). Gong runs third-party penetration tests, a bug bounty, and a Vulnerability Disclosure Program at vdp.gong.io (Gong security features).
🧑💼 How access control used to work
The classic rollout went like this. IT connected SSO, RevOps created users by hand, and every manager got broad access "for now". Six months later, nobody could say who could hear which calls. A departed rep's account was still active because nobody owned offboarding.
That was the real risk in conversation intelligence. The controls existed. They were simply switched on late, or not at all.
✅ What to switch on in week one
Use this list before the first call is recorded.
SSO, enforced. Turn off password login once SSO works.
SCIM provisioning. SCIM (System for Cross-domain Identity Management) creates and removes users from your identity provider, so leavers lose access the same day.
Permission profiles. Restrict call access by team. Sales managers rarely need every CS call.
Audit API export. Send logs to your security tool weekly, not only after an incident.
BYOK, if policy requires it. Bring your own key gives you control over encryption keys (Gong security features).
⚠️ What changed: agents need permissions too
Here is the shift most security reviews miss. In 2027, people are not the only actors touching call data. AI agents now read transcripts, draft emails, and update CRM fields. A role model built for humans does not tell you what an agent may do without asking.
Ask every vendor, Gong included, a direct question. Which AI features can write to our CRM or send messages on their own, and where is that logged?
🛡️ How Oliv AI splits agent permissions
Oliv AI builds the permission model into its two super-agents. Olivia, Oliv AI's Chief of AI Staff, works on an "Ask before acting" model for AEs, BDRs, AMs, and CS managers. Oliver, the Chief AI GTM Engineer, works on "Act without asking" for RevOps and sales leaders who own the playbook.
Oliv AI's agent harness lists guardrails, audit and security, and monitoring and logging as core parts. That gives your security team one place to see what an agent did and why. We designed it that way because a human role chart cannot govern software that acts.
"The Analyst agent allows me to understand everything I need with just one click, eliminating the long wait time I used to have with RevOps to get answers." Verified User Oliv AI G2 - Verified Review [6/17/2026]
Q6: Who Owns Call Recording Consent, and What Changes in Two-Party Consent States? [toc=6. Recording Consent]
Gong provides consent tools, but the customer stays accountable for recording consent.
The customer owns recording consent. Gong provides tools that help, including consent links, a personalized consent page, and audio prompt or Zoom-based consent options (Gong Trust Center). Gong's FAQ says sales calls can be recorded "in compliance with the right workflows", which leaves configuring those workflows to the customer (Gong security FAQ). In two-party (all-party) consent states such as California, every participant must agree. California's Invasion of Privacy Act (CIPA) allows $5,000 in statutory damages per violation (Holland & Knight).
📞 How consent used to work
For years, the standard answer was a line in the calendar invite and a "this call may be recorded" notice. Legal signed off once. Nobody checked whether the prompt fired on every platform, or for every guest who joined late.
That worked because lawsuits targeted the company on the call, and most claims went nowhere.
❌ What that cost
Now the targets have changed. Holland & Knight reported in July 2025 that class actions have begun to target AI call vendors, not only the businesses using them (Holland & Knight). Suits against Cresta and ConverseNow claim that AI tools captured and analyzed calls without valid consent (Holland & Knight, Fisher Phillips).
In August 2025, a federal court in Northern California denied ConverseNow's motion to dismiss a CIPA class action (Fisher Phillips). Commentators also question whether generic "may be monitored for quality" notices are enough once AI analysis is involved (Fisher Phillips). To be fair, results differ. In February 2025, a court dismissed a CIPA claim against Talkdesk because the calls were not private enough to support standing (Fisher Phillips).
I am not a lawyer, and this is not legal advice. Talk to counsel about the states and countries you sell into.
⏰ What changed with AI capture
Recording is no longer one Zoom call. Revenue teams now capture mobile calls, in-person meetings, and chat. Each new channel needs its own consent moment, or the risk travels with the data.
🎙️ How Oliv AI handles consent-first capture
Oliv AI captures context across five ways revenue teams communicate, including in-person meetings. For physical meetings, Oliv AI's partnership with Plaud brings what Oliv AI calls ambient, consent-first capture. The point is simple. Consent should be designed into the capture step, not added as a footer later.
Q7: How Does Gong Use Your Call Data for AI, and What Does the EU AI Act Change? [toc=7. AI Data Use and the EU AI Act]
Gong's DPA does not address whether customer data trains AI models (Gong DPA). Gong holds ISO 42001, the AI management system standard, earned in June 2025 (Gong responsible AI). Gong points customers to the AI section of its Trust Center for AI data practices (Gong security features, Gong Trust Center). The independent VerifyWise AI Trust Index grades Gong "B" and notes that public policy does not state whether inputs are kept out of model training (VerifyWise). Under the EU AI Act, workplace emotion recognition has been prohibited since February 2, 2025 (EU AI Act).
🤖 How AI review used to work
Two years ago, the AI question in a security review was one checkbox. Does the vendor use AI? Yes. Next question.
That was fine when AI meant a transcript and a keyword tracker. It is not fine when AI summarizes every deal, scores reps, and drafts customer emails.
❌ Where the gap is now
ISO 42001 proves that Gong runs an audited AI governance program (Gong responsible AI). It does not tell you whether your calls train a shared model. Even Gong's own AI governance post lists "Can I prevent certain data from being used in AI prompts and training?" as a question customers should ask (Gong AI governance). That is a good question. Ask it in writing.
Here is the AI rider language I would request in the order form.
Customer data is not used to train models shared with other customers.
Customer may opt out of AI features by workspace or team.
Gong lists every AI sub-processor and its region.
Gong gives notice before a new AI feature processes customer data.
⚖️ What the EU AI Act changes
The EU AI Act is Regulation (EU) 2024/1689 (EU AI Act). Article 5(1)(f) bans AI that infers the emotions of people at work, except for medical or safety reasons. That ban has applied since February 2, 2025 (EU AI Act). Article 50 transparency duties, which cover telling people about emotion recognition, apply from August 2, 2026 (EU AI Act).
For revenue teams, the practical question is narrow. Does any feature infer a rep's emotion from their voice? If your reps are in the EU, switch that feature off or get a written legal view. Text-only sentiment on emails is generally treated differently, but confirm it with counsel.
🧠 How Oliv AI approaches AI data use
Oliv AI runs more than 100 fine-tuned small language models (SLMs), each trained for one revenue question, such as pains, decision makers, or budget. Oliv AI reports under 1% hallucinations in production for this narrow design. Narrow models do one job, which makes "what does this model see and why" an easier question to answer in review.
"I love how Oliv AI goes beyond simple call transcription to actually interpret and extract actionable insights from every interaction." Verified User Oliv AI G2 - Verified Review [7/8/2026]
Q8: What Hidden Costs and Operational Risks Come With a Gong Security Setup? [toc=8. Hidden Costs and Risks]
Gong does not publish list prices, so security costs show up during negotiation. Vendr's Gong pricing data estimates dedicated regional hosting at $10,000 to $25,000 a year, custom compliance requirements at $15,000 to $50,000, and enhanced audit trails at $5,000 to $15,000 a year (Vendr). The same data puts custom SSO setup at $2,000 to $5,000 and SCIM setup at $1,000 to $3,000 (Vendr). Operational risks include CRM storage load from synced call data and the overhead of tracking sub-processor changes.
💸 How the bill used to look
A typical Gong budget covered seats and a platform fee. Security lived in a separate column that nobody priced. Then the EU team asked for regional hosting, legal asked for longer audit logs, and IT asked for custom SSO.
Each request was small. Together, they changed the deal.
💰 The add-on ranges to budget for
These are third-party estimates, not Gong list prices. Treat them as a starting point for negotiation (Vendr).
Estimated Gong Security Add-On Costs
Item
Estimated cost
Dedicated regional data residency
$10,000 to $25,000 a year
Custom compliance requirements
$15,000 to $50,000
Enhanced audit trails and reporting
$5,000 to $15,000 a year
Custom data retention configuration
$2,000 to $5,000
HIPAA BAA legal review
$1,000 to $3,000
Custom SSO provider setup
$2,000 to $5,000
SCIM provisioning setup
$1,000 to $3,000
One caution. Gong's help center now offers an EU data center choice to new customers (Gong security FAQ). Ask whether EU hosting is included for you before you accept any residency fee.
⚠️ The operational risks nobody prices
CRM storage load. Vendr's data cites a user report that Gong's Salesforce writes consumed their storage quota at 25MB a day (Vendr). Watch your storage after go-live.
Data flowing back. Getting call data back into the CRM can need extra work, as one reviewer notes below.
Sub-processor tracking. The 5 business day objection window needs someone watching it all year (Gong DPA).
"limitations of getting data back into salesforce" Verified User Gong - G2 Verified Review [5/21/2026]
🔄 What changed: the stack is the risk
Every bolt-on tool adds a DPA, a sub-processor list, a consent setup, and an audit log. The more apps you run, the more security reviews you repeat. Oliv AI's read is simple: RevOps built the stack, and the stack broke RevOps.
🧩 How Oliv AI cuts the review surface
Oliv AI is a revenue orchestration platform that runs agents on one GTM Context Graph, connected to 70+ apps including your CRM. Oliv AI prices its apps at about 30% of incumbent prices, so security and agent budget is not eaten by seats. One platform means one DPA, one sub-processor list, and one audit trail to review.
Q9: How Should RevOps Run a Gong Security Review Without Stalling the Deal? [toc=9. Security Review Checklist]
Run the security review in parallel with the deal, starting 90 days before go-live.
A Gong security review takes about 90 days when it runs in parallel with the commercial deal. RevOps should request the SOC 2 Type II report, ISO certificates, CAIQ, pentest summary, DPA, and sub-processor list in week one (Gong DPA, Gong Trust Center, Gong sub-processors). Security, privacy, and legal then review residency, AI training terms, recording consent, and deletion in that order. Starting 90 days before the target go-live date keeps lagging internal AI policies from stalling the rollout.
⏰ Why 90 days
Rashim Sethi, who sells Oliv AI into enterprise teams, put the cause plainly: "AI has moved so fast, companies' internal IT policies have not developed at that pace." Security teams are not slow on purpose. Many simply have no written policy for AI call bots yet.
So the review has two jobs. Check the vendor, and write the policy you are missing.
✅ The 90-day checklist
Days 1 to 10: collect the evidence
Request the Trust Center package: SOC 2 Type II, ISO 27001/27017/27018/27701/42001 certificates, CAIQ, and pentest summary (Gong Trust Center).
Download the current DPA and note its "last updated" date (Gong DPA).
Save a copy of the sub-processor list with today's date (Gong sub-processors).
Name one owner per DPA clause, using the table in Q1.
Days 11 to 40: ask the hard questions
Residency: US or EU data center, and is EU hosting included for you (Gong security FAQ)?
Consent: Which consent tools will you configure for each platform and state (Gong Trust Center)?
Access: Confirm SSO, SCIM, permission profiles, and Audit API export (Gong security features).
Retention: Set your retention period and confirm 30-day deletion after the term ends (Gong DPA, Gong security features).
Days 41 to 70: redline and decide
Legal adds the AI rider from Q7 and any breach notice hour count you need.
Privacy updates your records of processing and prospect notices.
Finance prices any residency, audit trail, or SSO add-ons from Q8 (Vendr).
Days 71 to 90: sign off and switch on
Security signs the risk acceptance memo.
IT enforces SSO and SCIM before the first recorded call.
RevOps sets a monthly check of the sub-processor page and CRM storage.
👥 Who owns each phase
Security Review Owners by Phase
Phase
Lead owner
Supporting owner
Evidence
RevOps
Security
Hard questions
Security
Privacy
Redlines
Legal
Finance
Switch on
IT
RevOps
💡 A simpler path
Oliv AI runs the same review with you, and its team supplies trust material at trust.oliv.ai up front. Oliv AI's published timeline is live by week 2, so the security work and the pilot can run side by side.
Q10: How Does an Agent-Based Platform Like Oliv Change the Security Review? [toc=10. Oliv and the Security Review]
Oliv AI is an AI-native revenue intelligence and revenue orchestration platform that runs agents on a single GTM Context Graph on top of your existing CRM. Oliv AI states it is SOC 2 Type II certified, GDPR and CCPA compliant, and encrypts data with AES-256 at rest and TLS 1.2+ in transit. Oliv AI publishes trust material at trust.oliv.ai and offers a full open export policy with no data lock-in. Reviewing one governed agent layer replaces reviewing several separate apps.
📚 How the review used to look
A mid-market revenue team in 2025 often ran a recorder, a forecasting tool, an engagement tool, and a CS platform. Each one meant a DPA, a sub-processor list, a SOC 2 report, and a consent setup. Security reviewed four vendors for one revenue process.
That is the Tool Trap in practice. The stack built to help the team became the thing security had to work around.
❌ What that cost
Every app copied the same call and CRM data into its own store. Every copy needed its own retention rule and deletion path. When a prospect asked to be forgotten, RevOps had to chase four systems.
The review did not get easier with each vendor. It got longer.
⚠️ What changed in 2027
AI agents now act on revenue data, not just display it. They update CRM fields, draft follow-ups, and flag deal risk. The security question moves from "who can see this call" to "what can this agent do, and who approved it".
That needs governance in the platform itself: permissions, approvals, memory controls, and traceability.
🧩 What Oliv AI does about it
Oliv AI builds governance into its agent harness. Here is how that maps to the review.
Oliv AI Security Review Answers
Review question
Oliv AI's answer
Certifications
SOC 2 Type II; GDPR and CCPA compliant
Encryption
AES-256 at rest, TLS 1.2+ in transit
Agent permissions
Olivia asks before acting; Oliver acts without asking for RevOps-owned rules
Audit
Harness includes audit and security, monitoring, and logging
Data exit
Full open export, no lock-in
Capture consent
Consent-first in-person capture through the Plaud partnership
Oliv AI also runs on top of Gong if you are mid-contract. You can review Oliv AI now and decide at renewal, with no overlap cost.
🗣️ What customers say
"It doesn't just record meetings; it automatically captures key insights, updates systems of record, identifies next steps, and helps keep teams aligned." Verified User Oliv AI G2 - Verified Review [6/23/2026]
"The only downside is that the platform can be a bit glitchy at times, but the support team is always quick to address and resolve any bugs." Verified User Oliv AI G2 - Verified Review [7/2/2026]
Oliv AI is not the right fit for everyone. If you only want call recording, or you run a B2C support team, a simpler recorder will do. If your security team is tired of reviewing the same data in four places, tell us what your review looks like. We will walk through it with you in seven minutes, no pitch.
A RevOps manager at Oliv AI was looking at website analytics one morning and noticed something odd. An enterprise prospect's team had skipped the pricing page entirely. They went straight to the footer, opened the privacy policy, and read it closely before they ever booked a call. That is how security review starts now. It starts before the first meeting, and it starts with the paperwork.
If you are reviewing Gong, here is the short answer. Gong's Data Processing Addendum (DPA) and certifications are a solid enterprise baseline. The real review work sits in five places: recording consent, AI data use, data residency, sub-processor tracking, and add-on cost. Most of that risk belongs to you, because under GDPR you are the controller. This guide walks through the September 2026 DPA in plain language and shows you what to check, who owns it, and how to finish the review without stalling the deal for a quarter.
Q1: What Is the Gong DPA and What Does It Actually Commit Gong To? [toc=1. What the Gong DPA Says]
Each time window in the Gong DPA needs a named owner on your side.
The Gong DPA is the Data Processing Addendum that forms part of Gong's terms and conditions. It names the customer as the controller and Gong as the processor of personal data in calls, emails, and CRM records. The version published on gong.io is marked "last updated September 2026" (Gong DPA). It sets transfer terms for the EU, UK, and Switzerland, a 5 business day window to object to new sub-processors, audit rights once a year on 45 days' notice, breach notice "without undue delay", and deletion of customer data 30 days after the contract ends (Gong DPA).
📄 Who does what under the DPA
A controller decides why and how personal data is used. A processor handles that data only on the controller's instructions. Under section 2.1 of the DPA, your company is the controller (the "business" under the California Consumer Privacy Act, or CCPA) and Gong is the processor (the "service provider") (Gong DPA).
There is one exception worth flagging. For Gong Enrich, the DPA's Schedule 2 makes Gong an independent controller of enrichment data (Gong DPA). If your team uses Enrich, that data sits under Gong's own privacy decisions, not only yours.
⚠️ The sensitive data line
Section 2.3 says the services "are not intended for the Processing of Sensitive Data" (Gong DPA). That is a statement of intent, not a technical block. Health details, financial account numbers, or union membership can still come up on a sales call. Your team carries the duty to keep that data out or to handle it lawfully under section 2.4 (Gong DPA).
⏰ The clause-to-action table
These are the time windows in the DPA that need a named owner on your side.
Gong DPA Clauses and Owners
DPA clause
What it says
Who should own it
Sub-processors (§5.2)
You may object within 5 business days of notice of a new sub-processor
Gong notifies "without undue delay"; details may arrive in phases
Incident response owner
Audit (§9.2)
Once a year, 45 days' written notice, except after a breach
Security lead, calendar the request
Deletion (§10)
All customer data deleted 30 days after termination or expiry; backups isolated
RevOps, plan exports before the end date
Changes (§14)
Either party may request changes on 45 days' notice; 30 days to agree
Legal
💡 What this means on Monday
The DPA gives you no hour count for breach notice. If your own policy needs one, such as 72 hours, ask for it in your order form. The 5 business day objection window is short, so the sub-processor page needs an owner, not a quarterly glance.
Oliv AI sees the same pattern in its own enterprise security reviews. The DPA is rarely what blocks a deal. The missing owner for each clause is. Oliv AI publishes its own trust material at trust.oliv.ai, so you can run the same clause-to-owner exercise on us side by side.
Q2: How Does Gong Handle GDPR, CCPA and International Data Transfers? [toc=2. GDPR, CCPA and Transfers]
Gong handles GDPR and CCPA through its DPA, which assigns the customer the controller role and Gong the processor role (Gong DPA). For data leaving the European Economic Area, the DPA uses the EU Standard Contractual Clauses (SCCs) under Decision 2021/914, Modules One to Four, governed by Irish law (Gong DPA). It adds the UK Addendum issued by the Information Commissioner's Office and a Swiss schedule under the Federal Act on Data Protection (FADP) (Gong DPA). Gong also states it is certified under the EU-U.S. Data Privacy Framework (Gong security FAQ).
🌍 The transfer stack, in plain words
Standard Contractual Clauses are pre-approved contract terms from the European Commission. They let personal data move to a country without an EU "adequacy" decision. Here is how Gong's stack lines up.
Gong Data Transfer Mechanisms by Region
Region
Mechanism in the Gong DPA
Source
EU and EEA
EU SCCs, Decision 2021/914, Modules One to Four, Irish law and courts
Part 4 of the schedule adds extra safeguards, including encryption in transit and at rest and rules for government access requests (Gong DPA).
⚖️ CCPA terms
Under section 2.5, Gong may not sell or share personal information as those terms are defined in the CCPA (Gong DPA). Gong processes data only on your documented instructions, and anonymization is listed as a permitted instruction under section 2.4 (Gong DPA).
✅ What stays with you as controller
Paper compliance on Gong's side does not move your duties. You still own these tasks.
Lawful basis. Decide and record why you process call data, such as legitimate interest or consent.
Data subject requests. Respond when a prospect asks to see or delete their data. Gong's FAQ points to API and in-app tools for the right to be forgotten (Gong security FAQ).
Notices. Tell prospects and employees that calls are recorded and analyzed.
Records of processing. List Gong and its sub-processors in your own records.
I have watched a privacy lead approve a vendor on the strength of its DPF certificate, then realize nobody owned deletion requests. The certificate was fine. The workflow was missing.
Oliv AI states that it is GDPR and CCPA compliant and offers a full open export policy with no data lock-in. That makes access and deletion requests simpler to answer, because the data is not trapped in one app's format.
Q3: Which Security Certifications Does Gong Hold in 2027, and How Do You Verify Them? [toc=3. Gong Security Certifications]
Gong's help center lists a SOC 2 Type II report, ISO/IEC 27001, 27017, 27018, and 27701 certificates, and a listing in the Cloud Security Alliance (CSA) STAR Registry (Gong security FAQ, Gong security features). Gong also lists ISO 42001:2023, the AI management system standard, which it says it earned in June 2025 (Gong security features, Gong responsible AI). Reports and certificates are available through the Gong Trust Center, where you request access before review (Gong Trust Center).
📋 What each certificate covers
Each certificate answers a different question. None of them answers all of them.
What Each Gong Certification Proves
Certification
What it shows
What it does not prove
SOC 2 Type II
An auditor tested security controls over a period of time
That your tenant settings are correct
ISO 27001
A managed information security system exists and is audited
Control depth for every product
ISO 27017 / 27018
Cloud security controls and protection of personal data in the cloud
Your consent workflow
ISO 27701
A privacy information management system on top of 27001
Lawful basis for your processing
ISO 42001
An audited AI governance program
Whether your calls train any model
CSA STAR
A published cloud security self-assessment or audit
Ongoing compliance between audits
🔍 How to verify, step by step
Request the package. Ask for the SOC 2 Type II report, ISO certificates, the CAIQ (the Cloud Security Alliance's standard security questionnaire), and the pentest summary through the Trust Center (Gong Trust Center).
Check the audit window. A SOC 2 Type II report covers a set period. Note the end date and ask for a bridge letter if it is older than six months.
Check scope. Confirm the products you buy, such as Engage or Forecast, sit inside the certified scope.
Check certificate dates. One 2025 third-party review said Gong's ISO 27001 certificate expired in October 2025. Gong's own pages now list ISO/IEC 27001:2022 (Gong Trust Center). Confirm the current certificate in the Trust Center rather than trusting any blog, including this one.
Log exceptions. Read the auditor's exceptions section, not only the opinion letter.
🧭 My honest read
Gong is a market leader, and it holds the certifications a market leader should hold. I would not build a security case against Gong on missing paperwork. The questions that matter sit in consent, AI data use, and residency, which the next sections cover.
Oliv AI is SOC 2 Type II certified and publishes its trust material at trust.oliv.ai. Ask Oliv AI for the same package you ask Gong for, and compare the audit windows and scope line by line.
Q4: Where Is Your Sales Data Stored and How Is It Protected? [toc=4. Data Storage and Protection]
Where Gong stores data and where it can be processed are two different questions.
Gong is hosted on Amazon Web Services (AWS). Gong's help center says new customers can choose US or EU data centers, with the US as the default (Gong security FAQ). Data is encrypted in transit with at least TLS 1.2 and at rest with AES-256, and customers can bring their own encryption key (BYOK) (Gong security features). Gong's offices in the US, Israel, and Ireland may process data, and its sub-processors sit in the US, UK, and EMEA (Gong security FAQ). Customer data is deleted within 30 days of contract end (Gong DPA, Gong security FAQ).
🗺️ How it used to work
For years, the standard answer on Gong storage was "it lives in the US." Many 2025 reviews, including the earlier version of this guide, said all customer data was stored in the United States. EU security teams treated that as a blocker or paid for workarounds.
That picture is now out of date. Gong's FAQ confirms the US and EU choice for new customers (Gong security FAQ). If you signed before that option existed, ask your account team in writing whether migration is possible and what it costs.
🔐 Storage is not the same as processing
Here is the part that catches teams out. Where data rests is one question. Where it can be accessed or processed is another.
Storage: US by default or EU on request, on AWS (Gong security FAQ).
Processing: Gong offices in the US, Israel, and Ireland (Gong security FAQ).
Retention: set by you and changeable at any time, per Gong's security page (Gong security features).
Deletion: 30 days after the contract ends, with backups isolated rather than wiped at once (Gong DPA).
⚠️ What changed with AI
Conversation intelligence used to mean a recording, a transcript, and a dashboard. Now each call feeds AI summaries, trackers, and agents. Every new AI feature can mean another processing step, and sometimes another sub-processor. The map of where your data travels grows each quarter, even if the storage region never changes.
Customer reviews show the operational side of this. One reviewer noted the cost of leaving.
"if you stop working with thew tool you lose the data" Verified User Gong - G2 Verified Review [3/19/2026]
"I cannot download all the data myself unless we upgrade the plan" Verified User Gong - G2 Verified Review [10/3/2025]
🧩 How Oliv AI approaches data flow
Oliv AI is an AI-native revenue intelligence platform that keeps account and deal context in one governed layer, the GTM Context Graph, instead of copying it across several bolt-on apps. Oliv AI encrypts data with AES-256 at rest and TLS 1.2+ in transit, and its open export policy means you keep your data when you leave. Fewer copies in fewer apps means a shorter data map for your security team to approve.
Q5: Which Access Controls and Audit Features Matter for an Enterprise Rollout? [toc=5. Access Controls and Audit]
Gong supports single sign-on (SSO) through SAML 2.0, OAuth 2.0, and OpenID Connect, plus SCIM provisioning for automatic user setup and removal (Gong security features). It ships four built-in roles (Collaborator, Standard user, Business administrator, and Technical administrator) and granular permission profiles by person, team, or group (Gong security features). The Gong Audit API exports activity logs in JSON, covering platform use and Gong staff access to customer data (Gong security features). Gong runs third-party penetration tests, a bug bounty, and a Vulnerability Disclosure Program at vdp.gong.io (Gong security features).
🧑💼 How access control used to work
The classic rollout went like this. IT connected SSO, RevOps created users by hand, and every manager got broad access "for now". Six months later, nobody could say who could hear which calls. A departed rep's account was still active because nobody owned offboarding.
That was the real risk in conversation intelligence. The controls existed. They were simply switched on late, or not at all.
✅ What to switch on in week one
Use this list before the first call is recorded.
SSO, enforced. Turn off password login once SSO works.
SCIM provisioning. SCIM (System for Cross-domain Identity Management) creates and removes users from your identity provider, so leavers lose access the same day.
Permission profiles. Restrict call access by team. Sales managers rarely need every CS call.
Audit API export. Send logs to your security tool weekly, not only after an incident.
BYOK, if policy requires it. Bring your own key gives you control over encryption keys (Gong security features).
⚠️ What changed: agents need permissions too
Here is the shift most security reviews miss. In 2027, people are not the only actors touching call data. AI agents now read transcripts, draft emails, and update CRM fields. A role model built for humans does not tell you what an agent may do without asking.
Ask every vendor, Gong included, a direct question. Which AI features can write to our CRM or send messages on their own, and where is that logged?
🛡️ How Oliv AI splits agent permissions
Oliv AI builds the permission model into its two super-agents. Olivia, Oliv AI's Chief of AI Staff, works on an "Ask before acting" model for AEs, BDRs, AMs, and CS managers. Oliver, the Chief AI GTM Engineer, works on "Act without asking" for RevOps and sales leaders who own the playbook.
Oliv AI's agent harness lists guardrails, audit and security, and monitoring and logging as core parts. That gives your security team one place to see what an agent did and why. We designed it that way because a human role chart cannot govern software that acts.
"The Analyst agent allows me to understand everything I need with just one click, eliminating the long wait time I used to have with RevOps to get answers." Verified User Oliv AI G2 - Verified Review [6/17/2026]
Q6: Who Owns Call Recording Consent, and What Changes in Two-Party Consent States? [toc=6. Recording Consent]
Gong provides consent tools, but the customer stays accountable for recording consent.
The customer owns recording consent. Gong provides tools that help, including consent links, a personalized consent page, and audio prompt or Zoom-based consent options (Gong Trust Center). Gong's FAQ says sales calls can be recorded "in compliance with the right workflows", which leaves configuring those workflows to the customer (Gong security FAQ). In two-party (all-party) consent states such as California, every participant must agree. California's Invasion of Privacy Act (CIPA) allows $5,000 in statutory damages per violation (Holland & Knight).
📞 How consent used to work
For years, the standard answer was a line in the calendar invite and a "this call may be recorded" notice. Legal signed off once. Nobody checked whether the prompt fired on every platform, or for every guest who joined late.
That worked because lawsuits targeted the company on the call, and most claims went nowhere.
❌ What that cost
Now the targets have changed. Holland & Knight reported in July 2025 that class actions have begun to target AI call vendors, not only the businesses using them (Holland & Knight). Suits against Cresta and ConverseNow claim that AI tools captured and analyzed calls without valid consent (Holland & Knight, Fisher Phillips).
In August 2025, a federal court in Northern California denied ConverseNow's motion to dismiss a CIPA class action (Fisher Phillips). Commentators also question whether generic "may be monitored for quality" notices are enough once AI analysis is involved (Fisher Phillips). To be fair, results differ. In February 2025, a court dismissed a CIPA claim against Talkdesk because the calls were not private enough to support standing (Fisher Phillips).
I am not a lawyer, and this is not legal advice. Talk to counsel about the states and countries you sell into.
⏰ What changed with AI capture
Recording is no longer one Zoom call. Revenue teams now capture mobile calls, in-person meetings, and chat. Each new channel needs its own consent moment, or the risk travels with the data.
🎙️ How Oliv AI handles consent-first capture
Oliv AI captures context across five ways revenue teams communicate, including in-person meetings. For physical meetings, Oliv AI's partnership with Plaud brings what Oliv AI calls ambient, consent-first capture. The point is simple. Consent should be designed into the capture step, not added as a footer later.
Q7: How Does Gong Use Your Call Data for AI, and What Does the EU AI Act Change? [toc=7. AI Data Use and the EU AI Act]
Gong's DPA does not address whether customer data trains AI models (Gong DPA). Gong holds ISO 42001, the AI management system standard, earned in June 2025 (Gong responsible AI). Gong points customers to the AI section of its Trust Center for AI data practices (Gong security features, Gong Trust Center). The independent VerifyWise AI Trust Index grades Gong "B" and notes that public policy does not state whether inputs are kept out of model training (VerifyWise). Under the EU AI Act, workplace emotion recognition has been prohibited since February 2, 2025 (EU AI Act).
🤖 How AI review used to work
Two years ago, the AI question in a security review was one checkbox. Does the vendor use AI? Yes. Next question.
That was fine when AI meant a transcript and a keyword tracker. It is not fine when AI summarizes every deal, scores reps, and drafts customer emails.
❌ Where the gap is now
ISO 42001 proves that Gong runs an audited AI governance program (Gong responsible AI). It does not tell you whether your calls train a shared model. Even Gong's own AI governance post lists "Can I prevent certain data from being used in AI prompts and training?" as a question customers should ask (Gong AI governance). That is a good question. Ask it in writing.
Here is the AI rider language I would request in the order form.
Customer data is not used to train models shared with other customers.
Customer may opt out of AI features by workspace or team.
Gong lists every AI sub-processor and its region.
Gong gives notice before a new AI feature processes customer data.
⚖️ What the EU AI Act changes
The EU AI Act is Regulation (EU) 2024/1689 (EU AI Act). Article 5(1)(f) bans AI that infers the emotions of people at work, except for medical or safety reasons. That ban has applied since February 2, 2025 (EU AI Act). Article 50 transparency duties, which cover telling people about emotion recognition, apply from August 2, 2026 (EU AI Act).
For revenue teams, the practical question is narrow. Does any feature infer a rep's emotion from their voice? If your reps are in the EU, switch that feature off or get a written legal view. Text-only sentiment on emails is generally treated differently, but confirm it with counsel.
🧠 How Oliv AI approaches AI data use
Oliv AI runs more than 100 fine-tuned small language models (SLMs), each trained for one revenue question, such as pains, decision makers, or budget. Oliv AI reports under 1% hallucinations in production for this narrow design. Narrow models do one job, which makes "what does this model see and why" an easier question to answer in review.
"I love how Oliv AI goes beyond simple call transcription to actually interpret and extract actionable insights from every interaction." Verified User Oliv AI G2 - Verified Review [7/8/2026]
Q8: What Hidden Costs and Operational Risks Come With a Gong Security Setup? [toc=8. Hidden Costs and Risks]
Gong does not publish list prices, so security costs show up during negotiation. Vendr's Gong pricing data estimates dedicated regional hosting at $10,000 to $25,000 a year, custom compliance requirements at $15,000 to $50,000, and enhanced audit trails at $5,000 to $15,000 a year (Vendr). The same data puts custom SSO setup at $2,000 to $5,000 and SCIM setup at $1,000 to $3,000 (Vendr). Operational risks include CRM storage load from synced call data and the overhead of tracking sub-processor changes.
💸 How the bill used to look
A typical Gong budget covered seats and a platform fee. Security lived in a separate column that nobody priced. Then the EU team asked for regional hosting, legal asked for longer audit logs, and IT asked for custom SSO.
Each request was small. Together, they changed the deal.
💰 The add-on ranges to budget for
These are third-party estimates, not Gong list prices. Treat them as a starting point for negotiation (Vendr).
Estimated Gong Security Add-On Costs
Item
Estimated cost
Dedicated regional data residency
$10,000 to $25,000 a year
Custom compliance requirements
$15,000 to $50,000
Enhanced audit trails and reporting
$5,000 to $15,000 a year
Custom data retention configuration
$2,000 to $5,000
HIPAA BAA legal review
$1,000 to $3,000
Custom SSO provider setup
$2,000 to $5,000
SCIM provisioning setup
$1,000 to $3,000
One caution. Gong's help center now offers an EU data center choice to new customers (Gong security FAQ). Ask whether EU hosting is included for you before you accept any residency fee.
⚠️ The operational risks nobody prices
CRM storage load. Vendr's data cites a user report that Gong's Salesforce writes consumed their storage quota at 25MB a day (Vendr). Watch your storage after go-live.
Data flowing back. Getting call data back into the CRM can need extra work, as one reviewer notes below.
Sub-processor tracking. The 5 business day objection window needs someone watching it all year (Gong DPA).
"limitations of getting data back into salesforce" Verified User Gong - G2 Verified Review [5/21/2026]
🔄 What changed: the stack is the risk
Every bolt-on tool adds a DPA, a sub-processor list, a consent setup, and an audit log. The more apps you run, the more security reviews you repeat. Oliv AI's read is simple: RevOps built the stack, and the stack broke RevOps.
🧩 How Oliv AI cuts the review surface
Oliv AI is a revenue orchestration platform that runs agents on one GTM Context Graph, connected to 70+ apps including your CRM. Oliv AI prices its apps at about 30% of incumbent prices, so security and agent budget is not eaten by seats. One platform means one DPA, one sub-processor list, and one audit trail to review.
Q9: How Should RevOps Run a Gong Security Review Without Stalling the Deal? [toc=9. Security Review Checklist]
Run the security review in parallel with the deal, starting 90 days before go-live.
A Gong security review takes about 90 days when it runs in parallel with the commercial deal. RevOps should request the SOC 2 Type II report, ISO certificates, CAIQ, pentest summary, DPA, and sub-processor list in week one (Gong DPA, Gong Trust Center, Gong sub-processors). Security, privacy, and legal then review residency, AI training terms, recording consent, and deletion in that order. Starting 90 days before the target go-live date keeps lagging internal AI policies from stalling the rollout.
⏰ Why 90 days
Rashim Sethi, who sells Oliv AI into enterprise teams, put the cause plainly: "AI has moved so fast, companies' internal IT policies have not developed at that pace." Security teams are not slow on purpose. Many simply have no written policy for AI call bots yet.
So the review has two jobs. Check the vendor, and write the policy you are missing.
✅ The 90-day checklist
Days 1 to 10: collect the evidence
Request the Trust Center package: SOC 2 Type II, ISO 27001/27017/27018/27701/42001 certificates, CAIQ, and pentest summary (Gong Trust Center).
Download the current DPA and note its "last updated" date (Gong DPA).
Save a copy of the sub-processor list with today's date (Gong sub-processors).
Name one owner per DPA clause, using the table in Q1.
Days 11 to 40: ask the hard questions
Residency: US or EU data center, and is EU hosting included for you (Gong security FAQ)?
Consent: Which consent tools will you configure for each platform and state (Gong Trust Center)?
Access: Confirm SSO, SCIM, permission profiles, and Audit API export (Gong security features).
Retention: Set your retention period and confirm 30-day deletion after the term ends (Gong DPA, Gong security features).
Days 41 to 70: redline and decide
Legal adds the AI rider from Q7 and any breach notice hour count you need.
Privacy updates your records of processing and prospect notices.
Finance prices any residency, audit trail, or SSO add-ons from Q8 (Vendr).
Days 71 to 90: sign off and switch on
Security signs the risk acceptance memo.
IT enforces SSO and SCIM before the first recorded call.
RevOps sets a monthly check of the sub-processor page and CRM storage.
👥 Who owns each phase
Security Review Owners by Phase
Phase
Lead owner
Supporting owner
Evidence
RevOps
Security
Hard questions
Security
Privacy
Redlines
Legal
Finance
Switch on
IT
RevOps
💡 A simpler path
Oliv AI runs the same review with you, and its team supplies trust material at trust.oliv.ai up front. Oliv AI's published timeline is live by week 2, so the security work and the pilot can run side by side.
Q10: How Does an Agent-Based Platform Like Oliv Change the Security Review? [toc=10. Oliv and the Security Review]
Oliv AI is an AI-native revenue intelligence and revenue orchestration platform that runs agents on a single GTM Context Graph on top of your existing CRM. Oliv AI states it is SOC 2 Type II certified, GDPR and CCPA compliant, and encrypts data with AES-256 at rest and TLS 1.2+ in transit. Oliv AI publishes trust material at trust.oliv.ai and offers a full open export policy with no data lock-in. Reviewing one governed agent layer replaces reviewing several separate apps.
📚 How the review used to look
A mid-market revenue team in 2025 often ran a recorder, a forecasting tool, an engagement tool, and a CS platform. Each one meant a DPA, a sub-processor list, a SOC 2 report, and a consent setup. Security reviewed four vendors for one revenue process.
That is the Tool Trap in practice. The stack built to help the team became the thing security had to work around.
❌ What that cost
Every app copied the same call and CRM data into its own store. Every copy needed its own retention rule and deletion path. When a prospect asked to be forgotten, RevOps had to chase four systems.
The review did not get easier with each vendor. It got longer.
⚠️ What changed in 2027
AI agents now act on revenue data, not just display it. They update CRM fields, draft follow-ups, and flag deal risk. The security question moves from "who can see this call" to "what can this agent do, and who approved it".
That needs governance in the platform itself: permissions, approvals, memory controls, and traceability.
🧩 What Oliv AI does about it
Oliv AI builds governance into its agent harness. Here is how that maps to the review.
Oliv AI Security Review Answers
Review question
Oliv AI's answer
Certifications
SOC 2 Type II; GDPR and CCPA compliant
Encryption
AES-256 at rest, TLS 1.2+ in transit
Agent permissions
Olivia asks before acting; Oliver acts without asking for RevOps-owned rules
Audit
Harness includes audit and security, monitoring, and logging
Data exit
Full open export, no lock-in
Capture consent
Consent-first in-person capture through the Plaud partnership
Oliv AI also runs on top of Gong if you are mid-contract. You can review Oliv AI now and decide at renewal, with no overlap cost.
🗣️ What customers say
"It doesn't just record meetings; it automatically captures key insights, updates systems of record, identifies next steps, and helps keep teams aligned." Verified User Oliv AI G2 - Verified Review [6/23/2026]
"The only downside is that the platform can be a bit glitchy at times, but the support team is always quick to address and resolve any bugs." Verified User Oliv AI G2 - Verified Review [7/2/2026]
Oliv AI is not the right fit for everyone. If you only want call recording, or you run a B2C support team, a simpler recorder will do. If your security team is tired of reviewing the same data in four places, tell us what your review looks like. We will walk through it with you in seven minutes, no pitch.
The Gong DPA is the Data Processing Addendum that forms part of Gong's terms and conditions. It sets out how Gong processes personal data from your calls, emails, and CRM records on your behalf. The version on gong.io is marked as last updated in September 2026.
Here is what it commits to, in plain terms:
Your company is the controller and Gong is the processor (the business and service provider under the CCPA).
You may object to a new sub-processor within 5 business days of notice.
Gong reports a breach without undue delay, with no fixed hour count.
You may audit once a year with 45 days' written notice.
Gong deletes customer data 30 days after the contract ends.
One exception matters. For Gong Enrich, Gong acts as an independent controller of enrichment data. We recommend that you give each clause a named owner on your side, because the short windows are easy to miss. Oliv AI runs the same clause-to-owner exercise in its own enterprise security reviews, and we find the missing owner, not the contract, is what usually slows a deal.
Is Gong GDPR compliant?
Gong supports GDPR compliance through its DPA, but compliance for your use of Gong stays with you as the controller. The DPA covers international transfers with several mechanisms:
EU Standard Contractual Clauses under Decision 2021/914, Modules One to Four, under Irish law.
The UK Addendum issued by the Information Commissioner's Office.
A Swiss schedule under the Federal Act on Data Protection.
Gong's certification under the EU-U.S. Data Privacy Framework.
What Gong cannot do for you is choose your lawful basis, answer every data subject request, or write your privacy notices. Gong provides API and in-app tools for the right to be forgotten, but someone on your team must own the request workflow.
We have seen privacy teams approve a vendor on its certificate and then discover nobody owned deletion requests. Oliv AI states that it is GDPR and CCPA compliant and offers a full open export policy, which makes access and deletion requests easier to answer. If you are weighing options, our Gong vs Oliv comparison covers how the two platforms handle data.
Where does Gong store customer data?
Gong is hosted on Amazon Web Services. According to Gong's help center, new customers can choose US or EU data centers, and the US is the default. Older reviews that say all Gong data stays in the US are now out of date.
Storage and processing are two different maps, so check both:
Storage: US by default or EU on request, on AWS.
Processing: Gong offices in the US, Israel, and Ireland may access data.
Sub-processors: located in the US, UK, and EMEA, listed on Gong's sub-processor page.
Encryption: at least TLS 1.2 in transit and AES-256 at rest, with bring-your-own-key support.
Deletion: 30 days after the contract ends.
If you signed before the EU option existed, ask your account team in writing whether you can migrate and what it costs. Every new AI feature can add a processing step, so ask for the AI sub-processor list too. Oliv AI keeps account and deal context in one governed layer instead of copying it across several apps, which shortens the data map. Our guide to stack consolidation explains why fewer copies matter.
Does Gong have SOC 2 Type II and ISO certifications?
Yes. Gong's help center lists a SOC 2 Type II report and ISO/IEC 27001, 27017, 27018, and 27701 certificates. Gong is also listed in the Cloud Security Alliance STAR Registry. It holds ISO 42001, the AI management system standard, which Gong says it earned in June 2025.
A certificate answers a narrow question, so verify it properly:
Request the SOC 2 report, ISO certificates, CAIQ questionnaire, and pentest summary through the Gong Trust Center.
Check the audit window and ask for a bridge letter if the report is older than six months.
Confirm the products you buy sit inside the certified scope.
Read the auditor's exceptions, not just the opinion letter.
Gong is a market leader and holds the certifications a market leader should hold. We would not build a case against Gong on missing paperwork. The harder questions sit in consent, AI data use, and residency. Oliv AI is SOC 2 Type II certified and shares its trust material up front, so you can compare audit windows side by side. See our Gong reviews analysis for what users say beyond the certificates.
Does Gong use customer call data to train its AI models?
Gong's DPA does not address AI model training. Gong holds ISO 42001, which shows it runs an audited AI governance program, but that standard does not promise your calls stay out of shared models. The independent VerifyWise AI Trust Index grades Gong B and notes that public policy does not state whether inputs are kept out of training.
Even Gong's own AI governance guidance suggests customers ask whether they can keep data out of AI prompts and training. We agree. Ask for these terms in writing in your order form:
Customer data is not used to train models shared with other customers.
You can opt out of AI features by workspace or team.
Gong lists every AI sub-processor and its region.
Gong gives notice before a new AI feature processes your data.
If you have reps in the EU, also check for features that infer emotion from voice. The EU AI Act has banned workplace emotion recognition since February 2, 2025. Oliv AI runs more than 100 narrow, fine-tuned small language models, each trained for one revenue question, which makes it easier to explain what each model sees. Read more in our agentic revenue intelligence guide.
Who is responsible for call recording consent when using Gong?
You are. Gong provides tools that help, including consent links, a personalized consent page, and audio prompt or Zoom-based consent options. Gong's FAQ says calls can be recorded in compliance with the right workflows, which means your team must configure those workflows.
The stakes are higher in two-party consent states such as California, where every participant must agree. California's Invasion of Privacy Act allows $5,000 in statutory damages per violation. Since 2025, class actions have also targeted AI call vendors, including suits against Cresta and ConverseNow.
A practical consent checklist:
Turn on a live audio or bot prompt for every meeting platform you use.
Decide what happens when a guest declines.
Keep records of consent.
Review consent for mobile calls and in-person meetings, not only video.
This is not legal advice, so involve counsel for the states and countries you sell into. Oliv AI designs consent into capture, including consent-first capture for in-person meetings through its Plaud partnership. Our article on Gong recording covers the recording setup in more detail.
How long does a Gong security review take?
A Gong security review usually takes about 90 days when it runs alongside the commercial deal. Many companies still lack a written policy for AI call tools, so the review often has to create one. Starting early stops lagging internal policies from stalling the rollout.
A simple four-phase plan works well:
Days 1 to 10: collect the SOC 2 report, ISO certificates, CAIQ, pentest summary, DPA, and sub-processor list.
Days 11 to 40: ask about residency, AI training, consent, access controls, and retention.
Days 41 to 70: legal redlines the AI rider and breach terms, and finance prices any add-ons.
Days 71 to 90: security signs off, and IT enforces single sign-on and SCIM before the first recorded call.
Budget for possible add-ons too. Vendr's Gong pricing data estimates regional hosting at $10,000 to $25,000 a year and enhanced audit trails at $5,000 to $15,000 a year. Oliv AI supplies its trust material at the start and publishes a live-by-week-two timeline, so the pilot and the review can run in parallel. Our Gong implementation timeline shows how the review fits into rollout.
Enjoyed the read? Join our founder for a quick 7-minute chat — no pitch, just a real conversation on how we’re rethinking RevOps with AI.
Still got questions?
Come discuss this article with me.
Hi, I'm Ishan, Founder and CEO of Oliv.
I'm always up for a conversation about revenue intelligence, AI agents, or what's actually working (and what's not) across revenue teams.
I'd love to hear your perspective.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.